Key tolerance and backup key
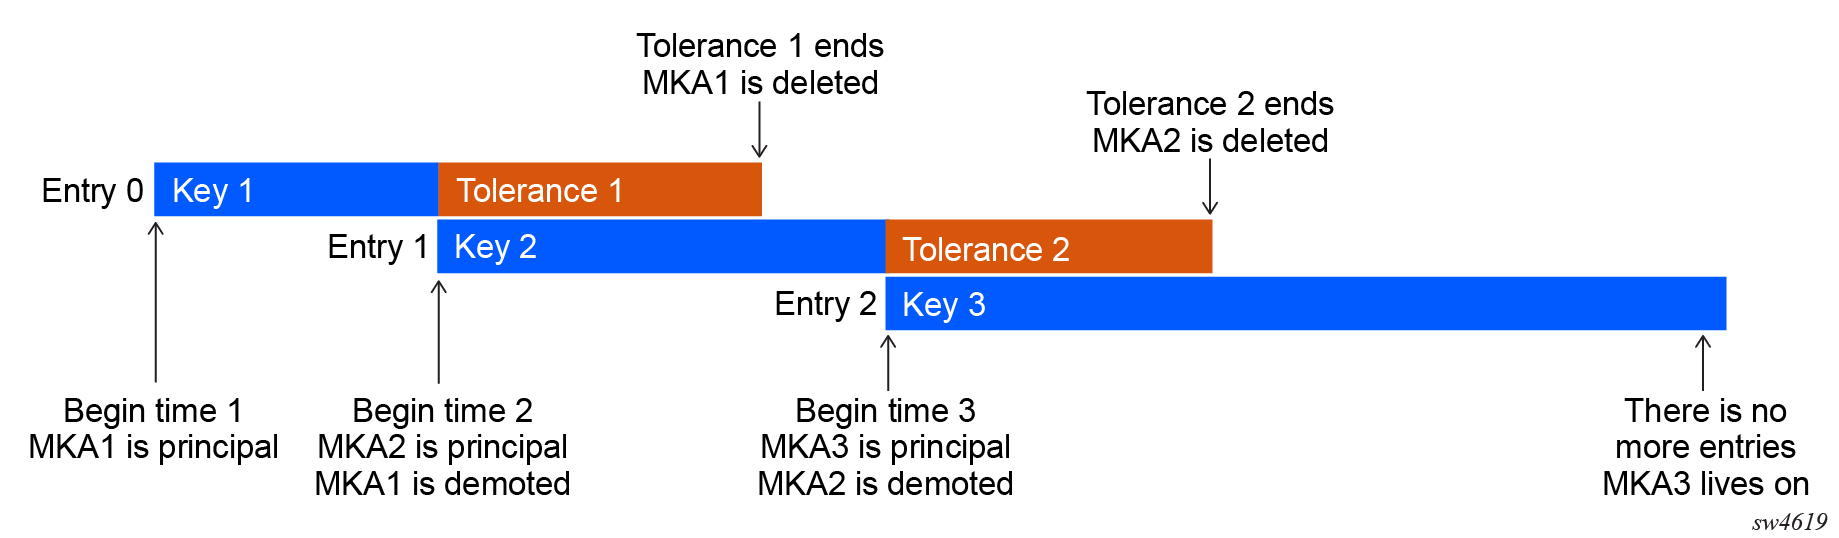
The MKA instance created by the first active key entry serves as the principal session from its begin time and remains functional until the end of its tolerance period. When the next key entry becomes active at its begin time, a new MKA instance is created. When the new MKA instance becomes operationally up, it becomes the principal session, and the MKA instance created by the first key entry becomes the backup session until its tolerance timer expires. If the principal session fails, the backup session takes over and becomes the principal. The switch from principal to backup session is seamless.
Unlike other applications that allow a keychain key entry tolerance of 0, MACsec requires a minimum tolerance of 20 seconds to allow time for the new MKA instance to become operationally up. If the new MKA session does not become operationally up by the time the tolerance of the first key entry expires, the MACsec sub-port becomes operationally down because neither the first nor second key entry has an operational MKA instance.
The following figure shows an example of tolerance with three key entries.
The 7705 SAR supports a maximum of three concurrent MKA sessions per sub-port at any one time, however, one of the sessions must be from key entry 0.
Key entry 0 is intended to be a permanent backup key and is the only key that can be configured with a tolerance of forever. This means the MKA session for Key 0 exchanges MKA hellos, but it is not intended to be the principal session.
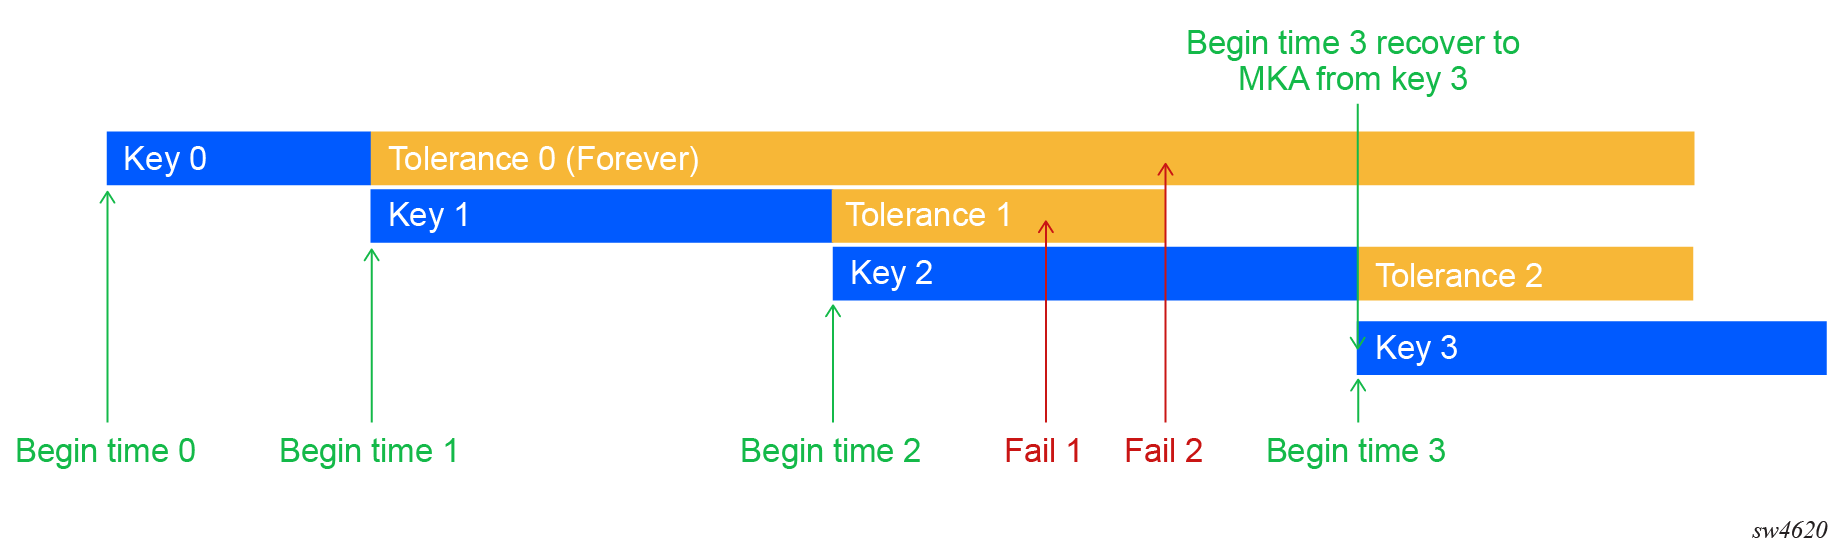
The following figure shows an example where key 0 is a backup key with the tolerance set to forever.
In this example:
-
If the MKA session of Key 1 fails or if Key 2 fails beyond Fail 2 point and before Begin time 3, the MKA session of Key 0 takes over as the principal MKA session.
-
At Fail point 1 of Key 2, the fallback is Key 1 because its tolerance has not expired.
-
At Fail point 2 of Key 2, the fallback key is the Key 0 backup key entry.
-
If at the end of the Key 1 Tolerance period, Key 2 has not established an MKA session (for example, Key 2 has a mismatch in its CKN between the peers), the Key 0 MKA session takes over and becomes the principal MKA session.