ANYsec service encryption
The 7705 SAR can encrypt a service using ANYsec and the IEEE 802.1AE encryption engine.
The following figure shows the difference between tunnel and service encryption. With tunnel encryption, all services traversing the tunnel are encrypted. In contrast, service encryption allows the user to choose a specific service for encryption using its own specific PSK and SAK. The LSP carrying the services can serve multiple services that are in clear text or encrypted.
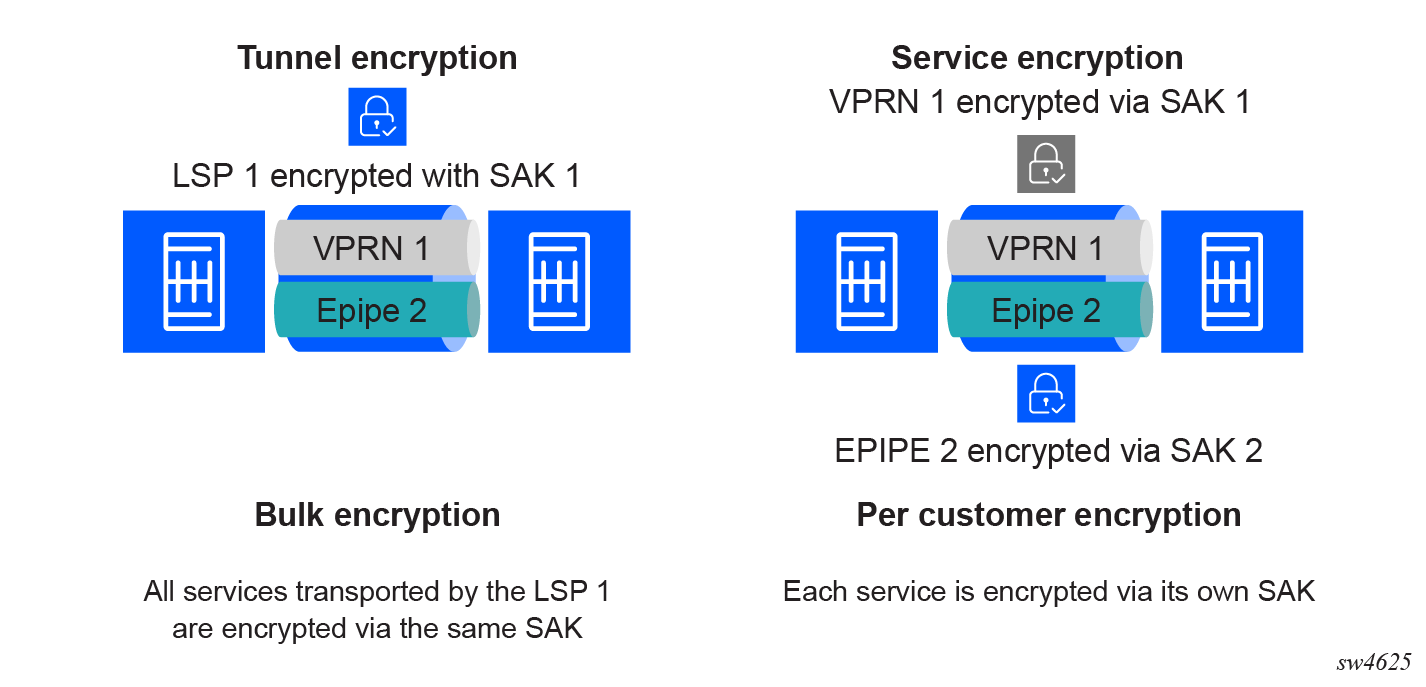
The 7705 SAR supports enabling both tunnel encryption and service encryption simultaneously on the same encrypted tunnel. This allows a service within the encrypted tunnel to be encrypted with its own specific SAK, while all other services traversing the tunnel are bulk-encrypted using a different SAK. For example, a provider can initially encrypt an entire tunnel with a single SAK, such that all traffic and services over that tunnel are encrypted using this SAK. Later , the provider might decide that one or more services traversing this encrypted tunnel need to be secured with their own specific SAKs and separated from the tunnel bulk encryption. The provider can then assign a unique encryption group to these services, forcing them to distribute their own SAKs via their dedicated MKA sessions. These services are then separated from the tunnel's bulk encryption, using their own MKA sessions for key distribution and unique SAKs for data encryption.
With service encryption, a tunnel can transport either encrypted or clear text services. When an encryption group is assigned to a service, that service becomes a secure service, and encryption is enabled for it. When encryption is enabled, the service only transmits and accepts encrypted traffic. Any clear text traffic is rejected and dropped.
ANYsec encryption is supported on the following services when the underlying protocol is SR IS-IS or SR-OSPF:
- spoke SDP
VPRN (Layer 3 spoke-SDP interface), IES (Layer 3 spoke-SDP interface), Cpipe, and Epipe (including PW-RED and PW-switching)
- autobind
VPRN BGP-IPVPN
ANYsec service encryption is only supported within a single area; it is not supported with inter-AS or interarea options B or C. ANYsec service encryption is possible with inter-AS option A, provided that encryption is terminated on the ASBR or ABR, and that encryption on the neighboring ASBR or ABR is restarted by assigning ANYsec to those services
ANYsec service encryption only supports global prefix SID ranges for segment routing.