EBGP Route Resolution to a Static Route
This chapter provides information about EBGP route resolution to a static route.
Topics in this chapter include:
Applicability
This chapter was initially written for SR OS Release 14.0.R7, but the CLI in the latest update of this chapter is based on SR OS Release 26.7.R2. EBGP route resolution to a static route is supported in SR OS Release 14.0.R1, and later.
Overview
The configuration in this chapter resembles the configuration in chapter Inter-AS VPRN Model C (Layer 3 Services), but in this chapter, the EBGP peering between the ASBRs is using loopback addresses instead of interface addresses.
Typically, service providers use interface IP addresses in EBGP sessions toward an Autonomous System Border Router (ASBR) of an untrusted ISP, but it is possible to use loopback addresses, such as system IP addresses. This requires the ASBRs to provide visibility on each other's loopback address; for example, by defining static routes. EBGP route resolution to a static route only works for ASBRs that are directly connected. As an alternative, MPLS (for example, RSVP-TE or LDP) can be configured on the interfaces between the ASBRs, which is the only viable solution when the peering ASBRs are multiple hops away.
Configuring MPLS on the interface toward an ASBR of an untrusted ISP is considered insecure. For directly connected ASBRs, EBGP route resolution to a static route mitigates these security issues. On each ASBR, static routes are configured toward the loopback address of the peer ASBR. Additionally, the following command enables labeled routes to be resolved via a static route:
configure
    router Base
        bgp
            next-hop-resolution
                labeled-routes
                    allow-static
                exit
            exit
        exit
Even with this feature enabled, the system first tries to resolve the BGP next-hop to LDP or RSVP LSPs before the IP route table is attempted. The option is supported for the following address families:
Labeled IPv4 routes
VPN-IPv4 and VPN-IPv6 routes
Configuration
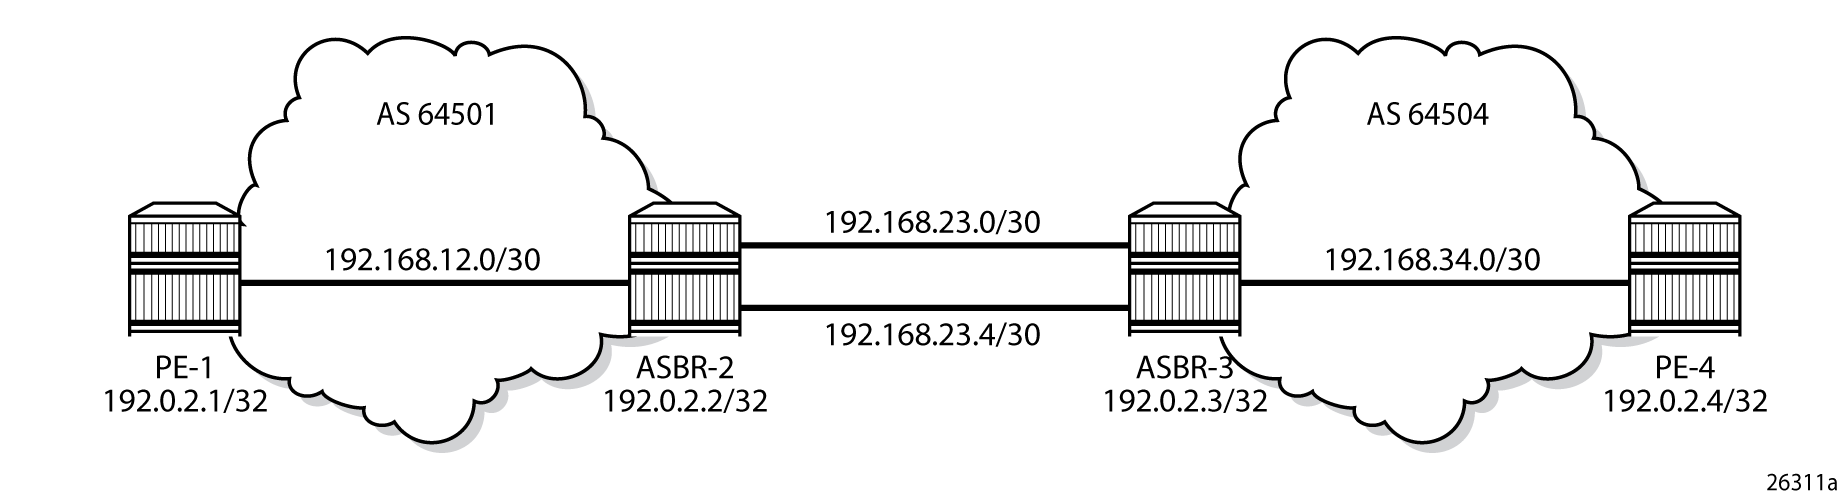
Example topology shows the example topology with four routers in two different ASs. ASBR-2 and ASBR-3 are connected via two links, which implies that there are multiple next-hops configured for the static route entry toward the loopback IP address of the EBGP peer. Also, Equal Cost Multi-Path (ECMP) and BGP multipath need to be enabled between these ASBRs.
The initial configuration on the nodes includes the following:
Cards, MDAs, ports
Router interfaces
IS-IS as IGP on the interfaces within an AS (alternatively, OSPF could be used)
LDP on the interfaces within an AS
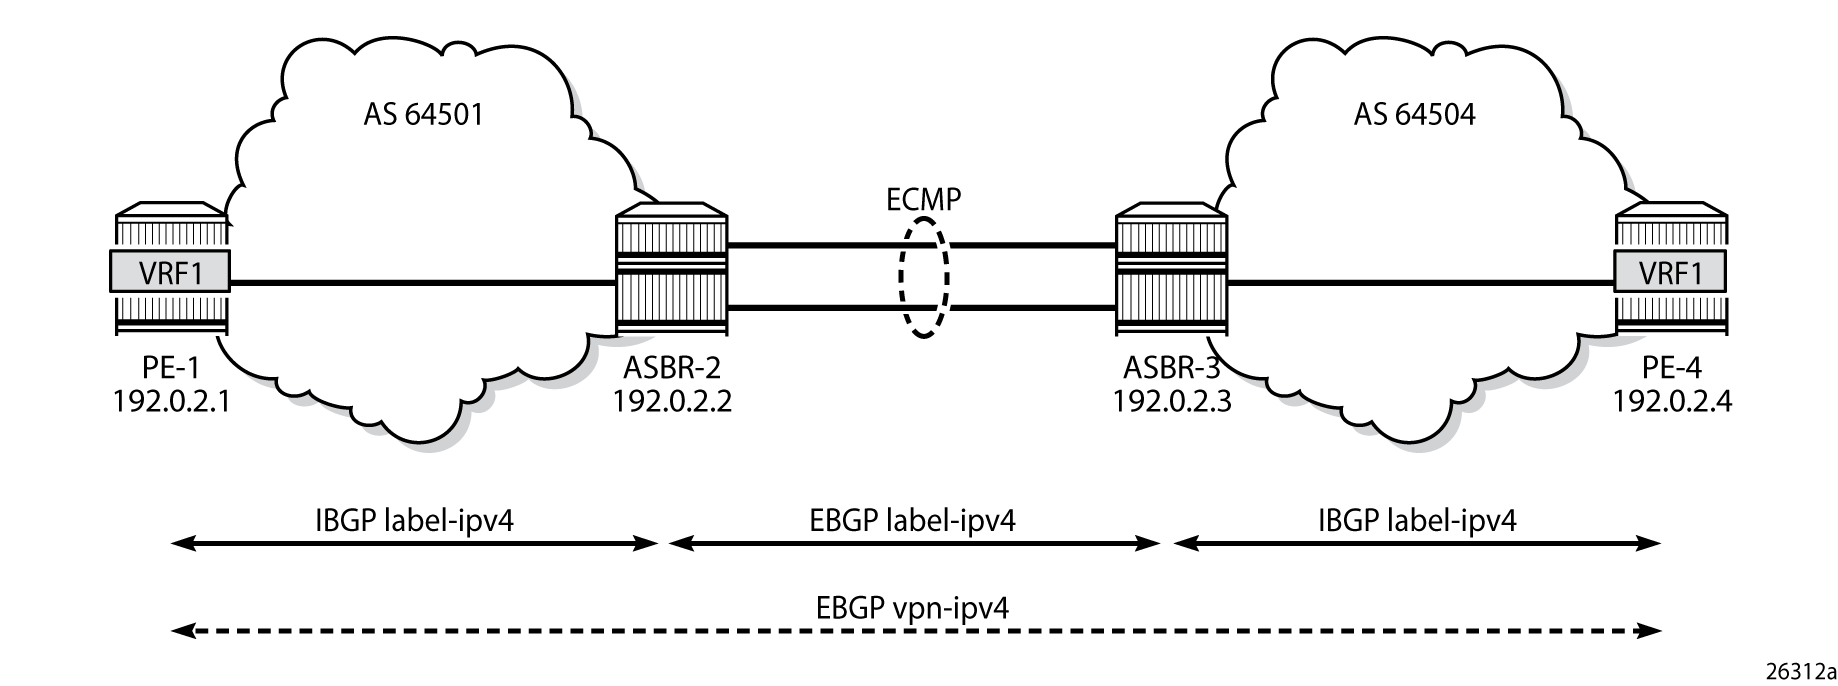
BGP peering shows the BGP sessions to be configured:
IBGP sessions for address family labeled IPv4 between the PEs within each AS
EBGP sessions for address family labeled IPv4 between ASBR-2 and ASBR-3
a multi-hop EBGP session for address family VPN-IPv4 between PE-1 and PE-4
On PE-1, IBGP is configured for address family labeled IPv4, as follows. The configuration on PE-4 is similar.
# on PE-1:
configure
    router Base
        autonomous-system 64501
        bgp
            split-horizon
            group "grp-IBGP"
                export "export-bgp"
                peer-as 64501
                neighbor 192.0.2.2
                    family label-ipv4
                exit
            exit
The following export policy exports the loopback IP prefixes from PE-1 to ASBR-2 (and from PE-4 to ASBR-3):
# on PE-1, PE-4:
configure
    router Base
        policy-options
            begin
            prefix-list "PE-sys"
                prefix 192.0.2.0/28 prefix-length-range 32-32
            exit
            policy-statement "export-bgp"
                entry 10
                    from
                        protocol direct
                        prefix-list "PE-sys"
                    exit
                    action accept
                    exit
                exit
            exit
            commit
On ASBR-2, IBGP and EBGP are configured for address family labeled IPv4, as follows. Two links are connecting ASBR-2 to ASBR-3 and, therefore, ECMP and BGP multipath are enabled. For more information about BGP multipath, see chapter BGP Multipath. The BGP configuration on ASBR-3 is similar.
# on ASBR-2:
configure
    router Base
        autonomous-system 64501
        ecmp 2
        bgp
            multi-path
                maximum-paths 2 ebgp 2
            exit
            split-horizon
            group "grp-EBGP"
                peer-as 64504
                neighbor 192.0.2.3
                    family label-ipv4
                    advertise-inactive
                exit
            exit
            group "grp-IBGP"
                peer-as 64501
                neighbor 192.0.2.1
                    family label-ipv4
                exit
            exit
        exit
On the ASBRs, the BGP routes with the loopback IP addresses of the local AS PEs are not active because IGP routes are preferred. The advertise-inactive option ensures that the ASBRs also advertise these inactive routes to each other. ASBR-2 advertises prefix 192.0.2.1/32 to ASBR-3; ASBR-3 advertises prefix 192.0.2.4/32 to ASBR-2. This way, no export policy is required for the EBGP session between ASBRs. However, no prefixes can be exchanged between the ASBRs because the EBGP session is not in the established state yet; they still lack routing to each other's loopback IP address.
Eventually, the labeled IPv4 routes for prefixes PE-1 and PE-4 will be exchanged between ASBRs and forwarded to the PEs in the peer AS. PE-1 will have a route toward PE-4 in its routing table, and PE-4 will have a route toward PE-1. Both PEs can then set up a multi-hop EBGP session to each other for address family VPN-IPv4; for example, on PE-1, as follows:
# on PE-1:
configure
    router Base
        bgp
            group "grp-EBGP-multihop"
                family vpn-ipv4
                peer-as 64504
                local-address 192.0.2.1
                neighbor 192.0.2.4
                    multihop 10
                    vpn-apply-export
                    export "EBGP-VPN-IPv4"
                exit
            exit
The export policy "EBGP-VPN-IPv4" is not required in this example, but usually some export policy would be used.
On PE-1, VPRN 1 is configured with loopback address 10.1.1.1/32, as follows:
# on PE-1:
configure
    service
        vprn 1 name "VPRN 1" customer 1 create
            interface "loopback" create
                address 10.1.1.1/32
                loopback
            exit
            bgp-ipvpn
                mpls
                    auto-bind-tunnel
                        resolution-filter
                            ldp
                        exit
                        resolution filter
                    exit
                    route-distinguisher 64501:1
                    vrf-target target:64501:1
                    no shutdown
                exit
            exit
            no shutdown
The configuration of PE-4 resembles the configuration of PE-1, whereas the configuration of ASBR-3 resembles that of ASBR-2.
This configuration is almost identical to the configuration in chapter Inter-AS VPRN Model C, with the difference that the EBGP session between the ASBRs does not use interface IP addresses, but loopback addresses. The problem is that the ASBRs cannot reach each other's loopback IP address, so the EBGP session between the ASBRs cannot be established, which can be verified in the BGP summary, as follows:
*A:ASBR-2# show router bgp summary all

===============================================================================
BGP Summary
===============================================================================
Legend : D - Dynamic Neighbor
===============================================================================
Neighbor
Description
ServiceId          AS PktRcvd InQ  Up/Down   State|Rcv/Act/Sent (Addr Family)
                      PktSent OutQ
-------------------------------------------------------------------------------
192.0.2.1
Def. Inst       64501       6    0 00h00m47s 1/0/0 (Lbl-IPv4)
                            5    0
192.0.2.3
Def. Inst       64504       0    0 00h00m47s Connect
                            0    0
The state of the BGP session toggles between Active and Connect. The last event is an openFail, as follows:
*A:ASBR-2# show router bgp neighbor 192.0.2.3 detail | match "BGP Neighbor" post-lines 16
BGP Neighbor
===============================================================================
-------------------------------------------------------------------------------
Peer                 : 192.0.2.3
Description          : (Not Specified)
Group                : grp-EBGP
-------------------------------------------------------------------------------
Peer AS              : 64504            Peer Port            : 0
Peer Address         : 192.0.2.3
Local AS             : 64501            Local Port           : 0
Local Address        : 0.0.0.0
Peer Type            : External         Dynamic Peer         : No
State                : Connect          Last State           : Active
Last Event           : openFail
Last Error           : Cease (Other Configuration Change)
AS Override          : Disabled
Local Family         : LABEL-IPv4
When the EBGP session between the ASBRs is not established, no IP prefixes are learned from the peer AS. This implies that PE-1 does not have a route toward PE-4 in its routing table. Therefore, no multi-hop EBGP session can be established between PE-1 and PE-4, which can be shown as follows:
*A:PE-1# show router route-table

===============================================================================
Route Table (Router: Base)
===============================================================================
Dest Prefix[Flags]                            Type    Proto     Age        Pref
      Next Hop[Interface Name]                                    Metric
-------------------------------------------------------------------------------
192.0.2.1/32                                  Local   Local     00h04m01s  0
       system                                                       0
192.0.2.2/32                                  Remote  ISIS      00h03m42s  15
       192.168.12.2                                                 10
192.168.12.0/30                               Local   Local     00h04m01s  0
       int-PE-1-ASBR-2                                              0
-------------------------------------------------------------------------------
No. of Routes: 3
Flags: n = Number of times nexthop is repeated
       B = BGP backup route available
       L = LFA nexthop available
       S = Sticky ECMP requested
===============================================================================
*A:PE-1# show router bgp summary all

===============================================================================
BGP Summary
===============================================================================
Legend : D - Dynamic Neighbor
===============================================================================
Neighbor
Description
ServiceId          AS PktRcvd InQ  Up/Down   State|Rcv/Act/Sent (Addr Family)
                      PktSent OutQ
-------------------------------------------------------------------------------
192.0.2.2
Def. Inst       64501      10    0 00h03m08s 0/0/1 (Lbl-IPv4)
                           11    0
192.0.2.4
Def. Inst       64504       0    0 00h02m33s Connect
                            0    0
The state of the multi-hop EBGP session toggles between Active and Connect. The last event is openFail, as follows:
*A:PE-1# show router bgp neighbor 192.0.2.4 detail | match "BGP Neighbor" post-lines 16
BGP Neighbor
===============================================================================
-------------------------------------------------------------------------------
Peer                 : 192.0.2.4
Description          : (Not Specified)
Group                : grp-EBGP-multihop
-------------------------------------------------------------------------------
Peer AS              : 64504            Peer Port            : 0
Peer Address         : 192.0.2.4
Local AS             : 64501            Local Port           : 0
Local Address        : 0.0.0.0
Peer Type            : External         Dynamic Peer         : No
State                : Connect          Last State           : Active
Last Event           : openFail
Last Error           : Unrecognized Error
AS Override          : Disabled
Local Family         : VPN-IPv4
The loopback IP addresses of the ASBRs can be made reachable by configuring static routes on each ASBR to the loopback IP address of the peer ASBR. This is sufficient to establish the EBGP session between the ASBRs, but no BGP labeled IPv4 routes are advertised to PE-1 and PE-4 yet. ASBR-2 and ASBR-3 are connected by two links and the static route entry contains two next-hops; for example, for ASBR-2, as follows. The configuration is similar for ASBR-3.
# on ASBR-2:
configure
    router Base
        static-route-entry 192.0.2.3/32
            next-hop 192.168.23.2
                no shutdown
            exit
            next-hop 192.168.23.6
                no shutdown
            exit
        exit
The routing table in ASBR-2 contains two routes toward ASBR-3, as follows:
*A:ASBR-2# show router route-table 192.0.2.3/32

===============================================================================
Route Table (Router: Base)
===============================================================================
Dest Prefix[Flags]                            Type    Proto     Age        Pref
      Next Hop[Interface Name]                                    Metric
-------------------------------------------------------------------------------
192.0.2.3/32                                  Remote  Static    00h00m00s  5
       192.168.23.2                                                 1
192.0.2.3/32                                  Remote  Static    00h00m00s  5
       192.168.23.6                                                 1
-------------------------------------------------------------------------------
No. of Routes: 2
Flags: n = Number of times nexthop is repeated
       B = BGP backup route available
       L = LFA nexthop available
       S = Sticky ECMP requested
===============================================================================
The EBGP session between the ASBRs is established; for example, on ASBR-2, as follows:
*A:ASBR-2# show router bgp summary all

===============================================================================
BGP Summary
===============================================================================
Legend : D - Dynamic Neighbor
===============================================================================
Neighbor
Description
ServiceId          AS PktRcvd InQ  Up/Down   State|Rcv/Act/Sent (Addr Family)
                      PktSent OutQ
-------------------------------------------------------------------------------
192.0.2.1
Def. Inst       64501      15    0 00h05m12s 1/0/0 (Lbl-IPv4)
                           14    0
192.0.2.3
Def. Inst       64504       6    0 00h00m56s 1/0/1 (Lbl-IPv4)
                            6    0
The ASBRs advertise labeled-IPv4 routes to each other, but these routes are not valid because the next-hop cannot be resolved. The ASBRs do not advertise these invalid received routes to PE-1 and PE-4. Therefore, the multi-hop EBGP session between PE-1 and PE-4 cannot be established yet. The state of the multi-hop EBGP session toggles between active and connect and the following output from PE-1 shows that the last event was openFail:
*A:PE-1# show router bgp neighbor 192.0.2.4 detail | match "BGP Neighbor" post-lines 16
BGP Neighbor
===============================================================================
-------------------------------------------------------------------------------
Peer                 : 192.0.2.4
Description          : (Not Specified)
Group                : grp-EBGP-multihop
-------------------------------------------------------------------------------
Peer AS              : 64504            Peer Port            : 0
Peer Address         : 192.0.2.4
Local AS             : 64501            Local Port           : 0
Local Address        : 0.0.0.0
Peer Type            : External         Dynamic Peer         : No
State                : Connect          Last State           : Active
Last Event           : openFail
Last Error           : Unrecognized Error
AS Override          : Disabled
Local Family         : VPN-IPv4
ASBR-2 advertised an inactive route for prefix 192.0.2.1/32 to ASBR-3 and received from ASBR-3 an inactive route for prefix 192.0.2.4/32. The following output shows that the route for prefix 192.0.2.4/32 is not valid on ASBR-2:
*A:ASBR-2# show router bgp routes label-ipv4
===============================================================================
 BGP Router ID:192.0.2.2        AS:64501       Local AS:64501
===============================================================================
 Legend -
 Status codes  : u - used, s - suppressed, h - history, d - decayed, * - valid
                 l - leaked, x - stale, > - best, b - backup, p - purge,
                 w - unused-weight-only
 Origin codes  : i - IGP, e - EGP, ? - incomplete

===============================================================================
BGP LABEL-IPV4 Routes
===============================================================================
Flag  Network                                            LocalPref   MED
      Nexthop (Router)                                   Path-Id     IGP Cost
      As-Path                                                        Label
-------------------------------------------------------------------------------
*i    192.0.2.1/32                                       100         None
      192.0.2.1                                          None        10
      No As-Path                                                     524285
i     192.0.2.4/32                                       None        None
      192.0.2.3                                          None        0
      64504                                                          524285
-------------------------------------------------------------------------------
Routes : 2
===============================================================================
Consequently, ASBR-2 does not advertise this invalid route to its IBGP peer PE-1 and PE-1 does not have a route toward PE-4 in its routing table, as follows:
*A:PE-1# show router route-table

===============================================================================
Route Table (Router: Base)
===============================================================================
Dest Prefix[Flags]                            Type    Proto     Age        Pref
      Next Hop[Interface Name]                                    Metric
-------------------------------------------------------------------------------
192.0.2.1/32                                  Local   Local     00h08m12s  0
       system                                                       0
192.0.2.2/32                                  Remote  ISIS      00h07m53s  15
       192.168.12.2                                                 10
192.168.12.0/30                               Local   Local     00h08m12s  0
       int-PE-1-ASBR-2                                              0
-------------------------------------------------------------------------------
No. of Routes: 3
Flags: n = Number of times nexthop is repeated
       B = BGP backup route available
       L = LFA nexthop available
       S = Sticky ECMP requested
===============================================================================
PE-1 and PE-4 cannot set up a multi-hop EBGP session to one another to exchange routes for VPRN 1. This problem can be solved in two different ways:
Enable LDP toward peer ASBR (alternatively, other MPLS tunnels can be used, such as RSVP-TE)
It is risky to enable MPLS toward a peer ASBR belonging to an untrusted ISP, but it is required between distant ASBRs if loopback addresses are used in EBGP peering.
In the following section, the first solution is described (LDP is enabled on the interfaces between the ASBRs); the section after that describes how to enable EBGP route resolution to a static route.
Enable LDP toward peer ASBR
LDP is configured on the interfaces between the ASBRs; for example, on ASBR-2, as follows. The configuration is similar on ASBR-3.
# on ASBR-2:
configure
    router Base
       ldp
            interface-parameters
                interface "int-ASBR-2-ASBR-3_1st" dual-stack
                    ipv4
                        no shutdown
                    exit
                    no shutdown
                exit
                interface "int-ASBR-2-ASBR-3_2nd" dual-stack
                    ipv4
                        no shutdown
                    exit
                    no shutdown
                exit
            exit
        exit
ASBR-2 now has a valid, best, and used route for prefix 192.0.2.4/32, as follows:
*A:ASBR-2# show router bgp routes label-ipv4
===============================================================================
 BGP Router ID:192.0.2.2        AS:64501       Local AS:64501
===============================================================================
 Legend -
 Status codes  : u - used, s - suppressed, h - history, d - decayed, * - valid
                 l - leaked, x - stale, > - best, b - backup, p - purge,
                 w - unused-weight-only
 Origin codes  : i - IGP, e - EGP, ? - incomplete

===============================================================================
BGP LABEL-IPV4 Routes
===============================================================================
Flag  Network                                            LocalPref   MED
      Nexthop (Router)                                   Path-Id     IGP Cost
      As-Path                                                        Label
-------------------------------------------------------------------------------
*i    192.0.2.1/32                                       100         None
      192.0.2.1                                          None        10
      No As-Path                                                     524285
u*>i  192.0.2.4/32                                       None        None
      192.0.2.3                                          None        1
      64504                                                          524285
-------------------------------------------------------------------------------
Routes : 2
===============================================================================
PE-1 has a valid route for prefix 192.0.2.4/32, as follows:
*A:PE-1# show router bgp routes label-ipv4
===============================================================================
 BGP Router ID:192.0.2.1        AS:64501       Local AS:64501
===============================================================================
 Legend -
 Status codes  : u - used, s - suppressed, h - history, d - decayed, * - valid
                 l - leaked, x - stale, > - best, b - backup, p - purge,
                 w - unused-weight-only
 Origin codes  : i - IGP, e - EGP, ? - incomplete

===============================================================================
BGP LABEL-IPV4 Routes
===============================================================================
Flag  Network                                            LocalPref   MED
      Nexthop (Router)                                   Path-Id     IGP Cost
      As-Path                                                        Label
-------------------------------------------------------------------------------
u*>i  192.0.2.4/32                                       100         None
      192.0.2.2                                          None        10
      64504                                                          524282
-------------------------------------------------------------------------------
Routes : 1
===============================================================================
The following routing table shows that PE-1 has a BGP labeled route toward PE-4:
*A:PE-1# show router route-table

===============================================================================
Route Table (Router: Base)
===============================================================================
Dest Prefix[Flags]                            Type    Proto     Age        Pref
      Next Hop[Interface Name]                                    Metric
-------------------------------------------------------------------------------
192.0.2.1/32                                  Local   Local     00h10m49s  0
       system                                                       0
192.0.2.2/32                                  Remote  ISIS      00h10m30s  15
       192.168.12.2                                                 10
192.0.2.4/32                                  Remote  BGP_LABEL 00h01m10s  170
       192.0.2.2 (tunneled)                                         10
192.168.12.0/30                               Local   Local     00h10m49s  0
       int-PE-1-ASBR-2                                              0
-------------------------------------------------------------------------------
No. of Routes: 4
Flags: n = Number of times nexthop is repeated
       B = BGP backup route available
       L = LFA nexthop available
       S = Sticky ECMP requested
===============================================================================
A multi-hop EBGP session is established for address family VPN-IPv4 between PE-1 and PE-4, as follows:
*A:PE-1# show router bgp summary all

===============================================================================
BGP Summary
===============================================================================
Legend : D - Dynamic Neighbor
===============================================================================
Neighbor
Description
ServiceId          AS PktRcvd InQ  Up/Down   State|Rcv/Act/Sent (Addr Family)
                      PktSent OutQ
-------------------------------------------------------------------------------
192.0.2.2
Def. Inst       64501      24    0 00h09m55s 1/1/1 (Lbl-IPv4)
                           24    0
192.0.2.4
Def. Inst       64504       7    0 00h01m06s 1/1/1 (VpnIPv4)
                            7    0
The loopback address defined in VPRN 1 on PE-4 (10.4.4.4/32) is advertised as VPN-IPv4 route in this multi-hop EBGP session on PE-1, as follows:
*A:PE-1# show router bgp routes vpn-ipv4
===============================================================================
 BGP Router ID:192.0.2.1        AS:64501       Local AS:64501
===============================================================================
 Legend -
 Status codes  : u - used, s - suppressed, h - history, d - decayed, * - valid
                 l - leaked, x - stale, > - best, b - backup, p - purge,
                 w - unused-weight-only
 Origin codes  : i - IGP, e - EGP, ? - incomplete

===============================================================================
BGP VPN-IPv4 Routes
===============================================================================
Flag  Network                                            LocalPref   MED
      Nexthop (Router)                                   Path-Id     IGP Cost
      As-Path                                                        Label
-------------------------------------------------------------------------------
u*>i  64504:1:10.4.4.4/32                                None        None
      192.0.2.4                                          None        0
      64504                                                          524285
-------------------------------------------------------------------------------
Routes : 1
===============================================================================
The routing table for VPRN 1 on PE-1 includes a BGP-VPN route to PE-4, as follows:
*A:PE-1# show router service-name "VPRN 1" route-table

===============================================================================
Route Table (Service: 1)
===============================================================================
Dest Prefix[Flags]                            Type    Proto     Age        Pref
      Next Hop[Interface Name]                                    Metric
-------------------------------------------------------------------------------
10.1.1.1/32                                   Local   Local     00h09m59s  0
       loopback                                                     0
10.4.4.4/32                                   Remote  BGP VPN   00h01m16s  170
       192.0.2.4 (tunneled:BGP)                                     1000
-------------------------------------------------------------------------------
No. of Routes: 2
Flags: n = Number of times nexthop is repeated
       B = BGP backup route available
       L = LFA nexthop available
       S = Sticky ECMP requested
===============================================================================
To restore the configuration, LDP is disabled on the interfaces between the ASBRs, as follows for ASBR-2. The configuration is similar on ASBR-3.
# on ASBR-2:
configure
    router Base
        ldp
            interface-parameters
                interface "int-ASBR-2-ASBR-3_1st" shutdown
                no interface "int-ASBR-2-ASBR-3_1st"
                interface "int-ASBR-2-ASBR-3_2nd" shutdown
                no interface "int-ASBR-2-ASBR-3_2nd"
            exit
EBGP route resolution to a static route
The static routes are already configured on both ASBRs and the EBGP session between the ASBRs is established.
Multi-hop EBGP labeled IPv4 route resolution to a static route needs to be enabled on ASBR-2 and ASBR-3 using the following command:
# on ASBR-2, ASBR-3:
configure
    router Base
        bgp
            next-hop-resolution
                labeled-routes
                    allow-static
                exit
            exit
        exit
On ASBR-2, the labeled IPv4 route for prefix 192.0.2.4/32 is now valid, best, and used, as follows:
*A:ASBR-2# show router bgp routes label-ipv4
===============================================================================
 BGP Router ID:192.0.2.2        AS:64501       Local AS:64501
===============================================================================
 Legend -
 Status codes  : u - used, s - suppressed, h - history, d - decayed, * - valid
                 l - leaked, x - stale, > - best, b - backup, p - purge,
                 w - unused-weight-only
 Origin codes  : i - IGP, e - EGP, ? - incomplete

===============================================================================
BGP LABEL-IPV4 Routes
===============================================================================
Flag  Network                                            LocalPref   MED
      Nexthop (Router)                                   Path-Id     IGP Cost
      As-Path                                                        Label
-------------------------------------------------------------------------------
*i    192.0.2.1/32                                       100         None
      192.0.2.1                                          None        10
      No As-Path                                                     524285
u*>i  192.0.2.4/32                                       None        None
      192.0.2.3                                          None        1
      64504                                                          524285
-------------------------------------------------------------------------------
Routes : 2
===============================================================================
PE-1 learns the following BGP labeled IPv4 route for prefix 192.0.2.4/32 from ASBR-2:
*A:PE-1# show router bgp routes label-ipv4
===============================================================================
 BGP Router ID:192.0.2.1        AS:64501       Local AS:64501
===============================================================================
 Legend -
 Status codes  : u - used, s - suppressed, h - history, d - decayed, * - valid
                 l - leaked, x - stale, > - best, b - backup, p - purge,
                 w - unused-weight-only
 Origin codes  : i - IGP, e - EGP, ? - incomplete

===============================================================================
BGP LABEL-IPV4 Routes
===============================================================================
Flag  Network                                            LocalPref   MED
      Nexthop (Router)                                   Path-Id     IGP Cost
      As-Path                                                        Label
-------------------------------------------------------------------------------
u*>i  192.0.2.4/32                                       100         None
      192.0.2.2                                          None        10
      64504                                                          524282
-------------------------------------------------------------------------------
Routes : 1
===============================================================================
The routing table on PE-1 contains a BGP labeled IPv4 route to 192.0.2.4/32:
*A:PE-1# show router route-table

===============================================================================
Route Table (Router: Base)
===============================================================================
Dest Prefix[Flags]                            Type    Proto     Age        Pref
      Next Hop[Interface Name]                                    Metric
-------------------------------------------------------------------------------
192.0.2.1/32                                  Local   Local     00h14m51s  0
       system                                                       0
192.0.2.2/32                                  Remote  ISIS      00h14m32s  15
       192.168.12.2                                                 10
192.0.2.4/32                                  Remote  BGP_LABEL 00h05m12s  170
       192.0.2.2 (tunneled)                                         10
192.168.12.0/30                               Local   Local     00h14m51s  0
       int-PE-1-ASBR-2                                              0
-------------------------------------------------------------------------------
No. of Routes: 4
Flags: n = Number of times nexthop is repeated
       B = BGP backup route available
       L = LFA nexthop available
       S = Sticky ECMP requested
===============================================================================
The multi-hop EBGP session between PE-1 in AS 64501 and PE-4 in AS 64504 is established, as follows:
*A:PE-1# show router bgp summary all

===============================================================================
BGP Summary
===============================================================================
Legend : D - Dynamic Neighbor
===============================================================================
Neighbor
Description
ServiceId          AS PktRcvd InQ  Up/Down   State|Rcv/Act/Sent (Addr Family)
                      PktSent OutQ
-------------------------------------------------------------------------------
192.0.2.2
Def. Inst       64501      32    0 00h13m53s 1/1/1 (Lbl-IPv4)
                           32    0
192.0.2.4
Def. Inst       64504      15    0 00h05m04s 1/1/1 (VpnIPv4)
                           15    0
The loopback address defined in VPRN 1 on PE-4 (10.4.4.4/32) is advertised as VPN-IPv4 route in this multi-hop EBGP session on PE-1, as follows:
*A:PE-1# show router bgp routes vpn-ipv4
===============================================================================
 BGP Router ID:192.0.2.1        AS:64501       Local AS:64501
===============================================================================
 Legend -
 Status codes  : u - used, s - suppressed, h - history, d - decayed, * - valid
                 l - leaked, x - stale, > - best, b - backup, p - purge,
                 w - unused-weight-only
 Origin codes  : i - IGP, e - EGP, ? - incomplete

===============================================================================
BGP VPN-IPv4 Routes
===============================================================================
Flag  Network                                            LocalPref   MED
      Nexthop (Router)                                   Path-Id     IGP Cost
      As-Path                                                        Label
-------------------------------------------------------------------------------
u*>i  64504:1:10.4.4.4/32                                None        None
      192.0.2.4                                          None        0
      64504                                                          524285
-------------------------------------------------------------------------------
Routes : 1
===============================================================================
The routing table for VPRN 1 on PE-1 includes the following BGP-VPN route to 10.4.4.4/32:
*A:PE-1# show router service-name "VPRN 1" route-table

===============================================================================
Route Table (Service: 1)
===============================================================================
Dest Prefix[Flags]                            Type    Proto     Age        Pref
      Next Hop[Interface Name]                                    Metric
-------------------------------------------------------------------------------
10.1.1.1/32                                   Local   Local     00h13m56s  0
       loopback                                                     0
10.4.4.4/32                                   Remote  BGP VPN   00h05m13s  170
       192.0.2.4 (tunneled:BGP)                                     1000
-------------------------------------------------------------------------------
No. of Routes: 2
Flags: n = Number of times nexthop is repeated
       B = BGP backup route available
       L = LFA nexthop available
       S = Sticky ECMP requested
===============================================================================
The results are similar on PE-4 and PE-1, and on ASBR-3 and ASBR-2.
For directly connected ASBRs, inter-AS VPRN model C can be configured using loopback addresses on the ASBRs without the need to enable MPLS between the ASBRs.
Conclusion
Most service providers use interface IP addresses in EBGP sessions, in which case this feature is not needed. However, some providers build directly connected EBGP sessions based on loopback interfaces. The loopback interface of the peer ASBR must be reachable and the labeled IPv4 routes for the remote AS PEs must be advertised to the local AS PEs. This advertisement can be achieved by configuring static routes on the ASBRs to the loopback address of their EBGP peer and enabling the EBGP route resolution to a static route. Enabling EBGP route resolution to a static route is much more secure than enabling MPLS on the interface to the peer ASBR of an untrusted ISP. However, when the ASBRs are distant and loopback addresses are used for the EBGP peering, MPLS must be enabled between the ASBRs.