BGP Prefix Limit per Address Family
This chapter provides information about BGP prefix limit per address family.
Topics in this chapter include:
Applicability
This chapter was initially written based on SR OS Release 15.0.R1, but the CLI in the latest update is based on SR OS Release 26.7.R1.
Overview
A BGP per address family prefix limit can be defined to control the number of prefixes learned per neighbor or per group of neighbors in the base router or in a VPRN. This feature allows ISPs to secure their network from misbehaving or misconfigured peers. This feature can also be used to enforce the terms of a service contract.
Supported address families for BGP prefix limit lists the address families for which a prefix limit can be defined in the base router and in VPRNs.
| Address family | Base router | VPRN |
|---|---|---|
| ipv4 | X | X |
| ipv6 | X | X |
| mcast-ipv4 | X | X |
| mcast-ipv6 | X | X |
| flow-ipv4 | X | X |
| flow-ipv6 | X | X |
| label-ipv4 | X | X |
| label-ipv6 | X | – |
| vpn-ipv4 | X | – |
| vpn-ipv6 | X | – |
| mvpn-ipv4 | X | – |
| mvpn-ipv6 | X | – |
| mcast-vpn-ipv4 | X | – |
| mcast-vpn-ipv6 | X | – |
| flow-vpn-ipv4 | X | – |
| flow-vpn-ipv6 | X | – |
| sr-policy-ipv4 | X | – |
| sr-policy-ipv6 | X | – |
| l2-vpn | X | – |
| mdt-safi | X | – |
| ms-pw | X | – |
| route-target | X | – |
| evpn | X | – |
| bgp-ls | X | – |
If the number of received routes from a peer exceeds a defined per address family limit, the BGP session is torn down, the state is changed to disabled, the routes learned from that peer are deleted, and the RIB and FIB are recalculated. With the log-only option enabled, the BGP session is not torn down and no routes are deleted. An SNMP trap message is issued when exceeding the per address family threshold (default: 90%), and the per address family prefix limit.
Re-establishing the BGP session with the peer requires a manual intervention, or use of the idle-timeout option. The idle-timeout option defines the time in minutes after which the system attempts to re-establish the BGP session. The idle-timeout option can be configured with the value forever or the idle-timeout option can be absent, which corresponds to the default behavior of requiring a manual intervention if the limit is exceeded.
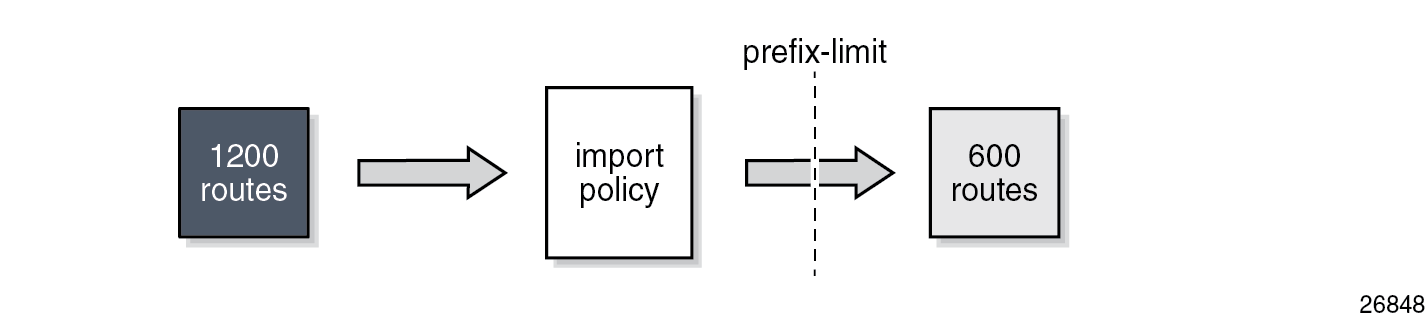
The post-import option indicates that the limit should be applied only to the routes accepted by import policies, as shown in Post-import option. A route rejected by an import policy is not counted when checking against the prefix limit. Not specifying the post-import option results in routes being counted and verified against the prefix limit when they are received, before the import policy is executed, and may lead to BGP sessions being torn down unexpectedly.
BGP sessions are torn down as soon as one of the address family prefix limits is exceeded, even when the limit for the other address family is not yet exceeded. In cases where this is important, consider defining two BGP sessions between two peers; the first using IPv4 for its transport, and the second using IPv6. In this way, an IPv4 limit being exceeded does not lead to IPv6 prefixes being affected.
Configuration
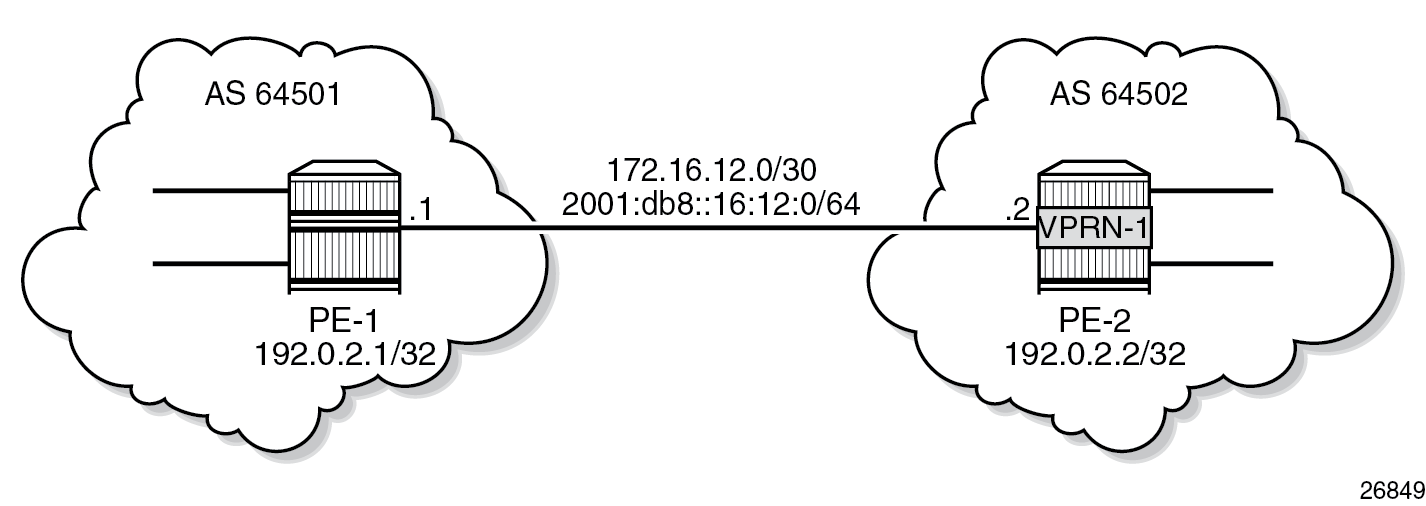
Example topology shows the example topology. PE-1 in AS 64501 peers with VPRN-1 hosted by PE-2 in AS 64502.
Two scenarios are considered:
Prefix limit without post-import option
PE-1 peers with VPRN-1 on PE-2, where IP prefix limit is configured in the BGP group toward PE-1: the IPv4 prefix limit is 10, the threshold is 50%, and the idle-timeout is 1 minute; the IPv6 prefix limit is 10, the threshold 80%, and the idle-timeout is 4 minutes, as follows:
# on PE-2:
configure
    service
        vprn 1 name "VPRN-1" customer 1 create
            description "VPRN with BGP prefix limit"
            autonomous-system 64502
            interface "int-VPRN-1_PE-2.1-PE-1" create
                address 172.16.12.2/30
                ipv6
                    address 2001:db8::16:12:2/126
                exit
                sap 1/1/c2/1:1 create
                exit
            exit
            bgp
                split-horizon
                loop-detect discard-route
                group "grp-EBGPv4-to-AS64501"
                    family ipv4
                    prefix-limit ipv4 10 threshold 50 idle-timeout 1
                    peer-as 64501
                    neighbor 172.16.12.1
                    exit
                exit
                group "grp-EBGPv6-to-AS64501"
                    family ipv6
                    prefix-limit ipv6 10 threshold 80 idle-timeout 4
                    peer-as 64501
                    neighbor 2001:db8::16:12:1
                    exit
                exit
                no shutdown
            exit
            no shutdown
The debug configuration is as follows:
debug
    router service-name "VPRN-1"
        bgp
            packets neighbor 172.16.12.1
            events neighbor 172.16.12.1
        exit
    exit
The debug output is sent to the log with log-id 1, as follows:
configure
    log
        log-id 1 name "log1"
            from debug-trace
            to memory
            no shutdown
        exit
Initially, the number of IPv4 routes received from PE-1 is below the threshold, and PE-1 gradually injects more IPv4 routes into VPRN-1 on PE-2. The following is a snapshot where three IPv4 routes and four IPv6 routes are received and active in PE-2:
*A:PE-2# show router service-name "VPRN-1" bgp summary
===============================================================================
 BGP Router ID:192.0.2.2        AS:64502       Local AS:64502
===============================================================================
BGP Admin State         : Up          BGP Oper State              : Up
Total Peer Groups       : 2           Total Peers                 : 2
Current Internal Groups : 2           Max Internal Groups         : 2
Total BGP Paths         : 7           Total Path Memory           : 2592
Memory Failures         : 0           Label Failures              : 0
Next Hop Failures       : 0           Backup Path Failures        : 0
Tunnel Failures         : 0           Tunnel Next Hop Failures    : 0

Total IPv4 Remote Rts   : 3           Total IPv4 Rem. Active Rts  : 3
Total IPv6 Remote Rts   : 4           Total IPv6 Rem. Active Rts  : 4
Total IPv4 Backup Rts   : 0           Total IPv6 Backup Rts       : 0
Total LblIpv4 Rem Rts   : 0           Total LblIpv4 Rem. Act Rts  : 0
Total LblIpv6 Rem Rts   : 0           Total LblIpv6 Rem. Act Rts  : 0
Total LblIpv4 Bkp Rts   : 0           Total LblIpv6 Bkp Rts       : 0
Total Supressed Rts     : 0           Total Hist. Rts             : 0
Total Decay Rts         : 0

Total McIPv4 Remote Rts : 0           Total McIPv4 Rem. Active Rts: 0
Total McIPv6 Remote Rts : 0           Total McIPv6 Rem. Active Rts: 0

Total FlowIpv4 Rem Rts  : 0           Total FlowIpv4 Rem Act Rts  : 0
Total FlowIpv6 Rem Rts  : 0           Total FlowIpv6 Rem Act Rts  : 0
Total FlowVpnv4 Rem Rts : 0           Total FlowVpnv4 Rem Act Rts : 0
Total FlowVpnv6 Rem Rts : 0           Total FlowVpnv6 Rem Act Rts : 0
Total Link State Rem Rts: 0           Total Link State Rem Act Rts: 0
Total SrPlcyIpv4 Rem Rts: 0           Total SrPlcyIpv4 Rem Act Rts: 0
Total SrPlcyIpv6 Rem Rts: 0           Total SrPlcyIpv6 Rem Act Rts: 0

===============================================================================
BGP Summary
===============================================================================
Legend : D - Dynamic Neighbor
===============================================================================
Neighbor
Description
                   AS PktRcvd InQ  Up/Down   State|Rcv/Act/Sent (Addr Family)
                      PktSent OutQ
-------------------------------------------------------------------------------
172.16.12.1
                64501       9    0 00h02m15s 3/3/0 (IPv4)
                            8    0
2001:db8::16:12:1
                64501       8    0 00h01m53s 4/4/0 (IPv6)
                            7    0
The following three BGP IPv4 routes are received by VPRN-1 on PE-2 and they are all active:
*A:PE-2# show router service-name "VPRN-1" bgp routes
===============================================================================
 BGP Router ID:192.0.2.2        AS:64502       Local AS:64502
===============================================================================
 Legend -
 Status codes  : u - used, s - suppressed, h - history, d - decayed, * - valid
                 l - leaked, x - stale, > - best, b - backup, p - purge,
                 w - unused-weight-only
 Origin codes  : i - IGP, e - EGP, ? - incomplete

===============================================================================
BGP IPv4 Routes
===============================================================================
Flag  Network                                            LocalPref   MED
      Nexthop (Router)                                   Path-Id     IGP Cost
      As-Path                                                        Label
-------------------------------------------------------------------------------
u*>i  10.1.0.0/24                                        None        None
      172.16.12.1                                        None        0
      64501                                                          -
u*>i  10.1.1.0/24                                        None        None
      172.16.12.1                                        None        0
      64501                                                          -
u*>i  10.1.2.0/24                                        None        None
      172.16.12.1                                        None        0
      64501                                                          -
-------------------------------------------------------------------------------
Routes : 3
===============================================================================
When the sixth BGP IPv4 route is received, the threshold value (50% of 10 is 5) is exceeded, and a message is generated and sent to log "99", as follows:
*A:PE-2# show log log-id "99"

===============================================================================
Event Log 99 log-name 99
===============================================================================
Description : Default System Log
Memory Log contents  [size=500   next event=127  (not wrapped)]

127 2026/09/03 08:51:19.250 UTC MINOR: BGP #2035 vprn1 Peer 2: 172.16.12.1
"(ASN 64501) VR 2: Group grp-EBGPv4-to-AS64501: Peer 172.16.12.1: number of routes learned has exceeded 50 percentage of the configured maximum (10) for ipv4 family"
*A:PE-2# show log log-id "99"

===============================================================================
---snip---

128 2026/09/03 08:52:50.250 UTC MINOR: BGP #2035 vprn1 Peer 2: 2001:db8::16:12:1
"(ASN 64501) VR 2: Group grp-EBGPv6-to-AS64501: Peer 2001:db8::16:12:1: number of routes learned has exceeded 80 percentage of the configured maximum (10) for ipv6 family"
When the eleventh BGP IPv4 route is received, the configured maximum number of BGP routes for IPv4 is exceeded. The BGP session state changes from established to idle and the peer is notified, as indicated in the following debug log:
*A:PE-2# show log log-id "log1"

===============================================================================
Event Log 1 log-name log1
===============================================================================
Description : (Not Specified)
Memory Log contents  [size=100   next event=49  (not wrapped)]

48 2026/09/03 08:55:43.250 UTC MINOR: DEBUG #2001 vprn1 Peer 2: 172.16.12.1
"Peer 2: 172.16.12.1: NOTIFICATION
Peer 2: 172.16.12.1 - Send BGP NOTIFICATION: Code = 6 (CEASE) Subcode = 1 (Maximum prefixed reached)
  Data Length = 7  Data: 0x0 0x1 0x1 0x0 0x0 0x0 0xa
"

47 2026/09/03 08:55:43.250 UTC MINOR: DEBUG #2001 vprn1 BGP
"BGP: STATE
Peer 2: 172.16.12.1 - Change State from ESTABLISHED to IDLE due to MAXPREFIX_EXCEEDED
"

46 2026/09/03 08:55:43.250 UTC MINOR: DEBUG #2001 vprn1 Peer 2: 172.16.12.1
"Peer 2: 172.16.12.1: UPDATE
Peer 2: 172.16.12.1 - Received BGP UPDATE:
    Withdrawn Length = 0
    Total Path Attr Length = 20
    Flag: 0x40 Type: 1 Len: 1 Origin: 0
    Flag: 0x40 Type: 2 Len: 6 AS Path:
        Type: 2 Len: 1 < 64501 >
    Flag: 0x40 Type: 3 Len: 4 Nexthop: 172.16.12.1
    NLRI: Length = 44
        10.1.0.0/24
        10.1.1.0/24
        10.1.2.0/24
        10.1.3.0/24
        10.1.4.0/24
        10.1.5.0/24
        10.1.6.0/24
        10.1.7.0/24
        10.1.8.0/24
        10.1.9.0/24
        10.1.10.0/24
"
The BGP session is torn down and the corresponding state is disabled, as follows:
*A:PE-2# show router service-name "VPRN-1" bgp summary
===============================================================================
 BGP Router ID:192.0.2.2        AS:64502       Local AS:64502
===============================================================================
BGP Admin State         : Up          BGP Oper State              : Up
Total Peer Groups       : 2           Total Peers                 : 2
Current Internal Groups : 1           Max Internal Groups         : 2
Total BGP Paths         : 6           Total Path Memory           : 2216
Memory Failures         : 0           Label Failures              : 0
Next Hop Failures       : 0           Backup Path Failures        : 0
Tunnel Failures         : 0           Tunnel Next Hop Failures    : 0

Total IPv4 Remote Rts   : 0           Total IPv4 Rem. Active Rts  : 0
Total IPv6 Remote Rts   : 10          Total IPv6 Rem. Active Rts  : 10
Total IPv4 Backup Rts   : 0           Total IPv6 Backup Rts       : 0
Total LblIpv4 Rem Rts   : 0           Total LblIpv4 Rem. Act Rts  : 0
Total LblIpv6 Rem Rts   : 0           Total LblIpv6 Rem. Act Rts  : 0
Total LblIpv4 Bkp Rts   : 0           Total LblIpv6 Bkp Rts       : 0
Total Supressed Rts     : 0           Total Hist. Rts             : 0
Total Decay Rts         : 0

Total McIPv4 Remote Rts : 0           Total McIPv4 Rem. Active Rts: 0
Total McIPv6 Remote Rts : 0           Total McIPv6 Rem. Active Rts: 0

Total FlowIpv4 Rem Rts  : 0           Total FlowIpv4 Rem Act Rts  : 0
Total FlowIpv6 Rem Rts  : 0           Total FlowIpv6 Rem Act Rts  : 0
Total FlowVpnv4 Rem Rts : 0           Total FlowVpnv4 Rem Act Rts : 0
Total FlowVpnv6 Rem Rts : 0           Total FlowVpnv6 Rem Act Rts : 0
Total Link State Rem Rts: 0           Total Link State Rem Act Rts: 0
Total SrPlcyIpv4 Rem Rts: 0           Total SrPlcyIpv4 Rem Act Rts: 0
Total SrPlcyIpv6 Rem Rts: 0           Total SrPlcyIpv6 Rem Act Rts: 0

===============================================================================
BGP Summary
===============================================================================
Legend : D - Dynamic Neighbor
===============================================================================
Neighbor
Description
                   AS PktRcvd InQ  Up/Down   State|Rcv/Act/Sent (Addr Family)
                      PktSent OutQ
-------------------------------------------------------------------------------
172.16.12.1
                64501       0    0 00h01m00s Disabled
                            0    0
2001:db8::16:12:1
                64501      23    0 00h08m27s 10/10/0 (IPv6)
                           20    0
Also, this event is recorded in the system logs, as follows:
*A:PE-2# show log log-id "99"

===============================================================================
Event Log 99 log-name 99
===============================================================================
Description : Default System Log
Memory Log contents  [size=500   next event=132  (not wrapped)]

140 2026/09/03 08:55:43.254 UTC WARNING: BGP #2012 vprn1 Peer 2: 172.16.12.1
"(ASN 64501) Peer 2: 172.16.12.1: Closing connection: VR 2: Group grp-EBGPv4-to-AS64501: Peer 172.16.12.1 not enabled or not in configuration"

139 2026/09/03 08:55:43.250 UTC WARNING: BGP #2005 vprn1 Peer 2: 172.16.12.1
"(ASN 64501) VR 2: Group grp-EBGPv4-to-AS64501: Peer 172.16.12.1: sending notification: code CEASE subcode MAX_PFX_RCHD"

138 2026/09/03 08:55:43.250 UTC WARNING: BGP #2039 vprn1 Peer 2: 172.16.12.1
"(ASN 64501) VR 2: Group grp-EBGPv4-to-AS64501: Peer 172.16.12.1: moved from higher state ESTABLISHED to lower state IDLE due to event MAXPREFIX_EXCEEDED"

137 2026/09/03 08:55:43.250 UTC MINOR: BGP #2034 vprn1 Peer 2: 172.16.12.1
"(ASN 64501) VR 2: Group grp-EBGPv4-to-AS64501: Peer 172.16.12.1: number of routes learned has exceeded configured maximum (10) for ipv4 family"

136 2026/09/03 08:55:43.250 UTC MINOR: BGP #2035 vprn1 Peer 2: 172.16.12.1
"(ASN 64501) VR 2: Group grp-EBGPv4-to-AS64501: Peer 172.16.12.1: number of routes learned has exceeded 50 percentage of the configured maximum (10) for ipv4 family"
When the idle-timeout expires, in this case, after one minute, the system tries to re-establish the session. With the BGP session re-established, the peer starts re-advertising its routes. As long as the number of received routes in VPRN-1 on PE-2 is lower than or equal to the limit, the session is maintained. In this example, the maximum number of received IPv4 routes is 10.
In the preceding example, IPv4 was the only address family configured for the BGP group that was torn down. When there are several address families in the same BGP group, the other address families are also impacted.
Prefix limit with post-import option
Use caution when using the prefix limit in combination with import policies. By default, the routes are counted when receiving them, that is, before the import policy is enforced. To postpone the prefix limit check, the post-import option must be used.
The BGP configuration for VPRN-1 on PE-2 is then adapted as follows:
# on PE-2:
configure
    service
        vprn "VPRN-1"
            bgp
                loop-detect discard-route
                split-horizon
                group "grp-EBGPv4-to-AS64501"
                    family ipv4
                    prefix-limit ipv4 10 threshold 50 idle-timeout 1 post-import
                    import "import-10.1-ranges"
                    peer-as 64501
                    neighbor 172.16.12.1
                    exit
                exit
                group "grp-EBGPv6-to-AS64501"
                    family ipv6
                    no prefix-limit ipv6      # no prefix limit for IPv6 anymore
                    peer-as 64501
                    neighbor 2001:db8::16:12:1
                    exit
                exit
                no shutdown
            exit
The import-10.1-ranges policy is defined as follows:
# on PE-2:
configure
    router Base
        policy-options
            begin
            prefix-list "pfx-10.1-ranges"
                prefix 10.1.0.0/16 longer
            exit
            policy-statement "import-10.1-ranges"
                entry 10
                    from
                        prefix-list "pfx-10.1-ranges"
                    exit
                    action accept
                    exit
                exit
                default-action drop
                exit
            exit
            commit
When twelve IPv4 routes are received over this BGP session, six in the 10.1.0.0/16 range and six in the 10.2.0.0/16 range, then only the six routes in the 10.1.0.0/16 range are accepted and active in the routing table, as follows:
*A:PE-2# show router service-name "VPRN-1" route-table protocol bgp

===============================================================================
Route Table (Service: 1)
===============================================================================
Dest Prefix[Flags]                            Type    Proto     Age        Pref
      Next Hop[Interface Name]                                    Metric
-------------------------------------------------------------------------------
10.1.0.0/24                                   Remote  BGP       00h03m02s  170
       172.16.12.1                                                  0
10.1.1.0/24                                   Remote  BGP       00h03m02s  170
       172.16.12.1                                                  0
10.1.2.0/24                                   Remote  BGP       00h03m02s  170
       172.16.12.1                                                  0
10.1.3.0/24                                   Remote  BGP       00h03m02s  170
       172.16.12.1                                                  0
10.1.4.0/24                                   Remote  BGP       00h03m02s  170
       172.16.12.1                                                  0
10.1.5.0/24                                   Remote  BGP       00h03m02s  170
       172.16.12.1                                                  0
-------------------------------------------------------------------------------
No. of Routes: 6
Flags: n = Number of times nexthop is repeated
       B = BGP backup route available
       L = LFA nexthop available
       S = Sticky ECMP requested
===============================================================================
The BGP session remains established with twelve received routes and six of these being active, as follows:
*A:PE-2# show router service-name "VPRN-1" bgp summary
===============================================================================
 BGP Router ID:192.0.2.2        AS:64502       Local AS:64502
===============================================================================
BGP Admin State         : Up          BGP Oper State              : Up
Total Peer Groups       : 2           Total Peers                 : 2
Current Internal Groups : 2           Max Internal Groups         : 2
Total BGP Paths         : 6           Total Path Memory           : 2216
Memory Failures         : 0           Label Failures              : 0
Next Hop Failures       : 0           Backup Path Failures        : 0
Tunnel Failures         : 0           Tunnel Next Hop Failures    : 0

Total IPv4 Remote Rts   : 12          Total IPv4 Rem. Active Rts  : 6
Total IPv6 Remote Rts   : 0           Total IPv6 Rem. Active Rts  : 0
Total IPv4 Backup Rts   : 0           Total IPv6 Backup Rts       : 0
Total LblIpv4 Rem Rts   : 0           Total LblIpv4 Rem. Act Rts  : 0
Total LblIpv6 Rem Rts   : 0           Total LblIpv6 Rem. Act Rts  : 0
Total LblIpv4 Bkp Rts   : 0           Total LblIpv6 Bkp Rts       : 0
Total Supressed Rts     : 0           Total Hist. Rts             : 0
Total Decay Rts         : 0

Total McIPv4 Remote Rts : 0           Total McIPv4 Rem. Active Rts: 0
Total McIPv6 Remote Rts : 0           Total McIPv6 Rem. Active Rts: 0

Total FlowIpv4 Rem Rts  : 0           Total FlowIpv4 Rem Act Rts  : 0
Total FlowIpv6 Rem Rts  : 0           Total FlowIpv6 Rem Act Rts  : 0
Total FlowVpnv4 Rem Rts : 0           Total FlowVpnv4 Rem Act Rts : 0
Total FlowVpnv6 Rem Rts : 0           Total FlowVpnv6 Rem Act Rts : 0
Total Link State Rem Rts: 0           Total Link State Rem Act Rts: 0
Total SrPlcyIpv4 Rem Rts: 0           Total SrPlcyIpv4 Rem Act Rts: 0
Total SrPlcyIpv6 Rem Rts: 0           Total SrPlcyIpv6 Rem Act Rts: 0

===============================================================================
BGP Summary
===============================================================================
Legend : D - Dynamic Neighbor
===============================================================================
Neighbor
Description
                   AS PktRcvd InQ  Up/Down   State|Rcv/Act/Sent (Addr Family)
                      PktSent OutQ
-------------------------------------------------------------------------------
172.16.12.1
                64501      16    0 00h04m36s 12/6/0 (IPv4)
                           13    0
2001:db8::16:12:1
                64501      40    0 00h16m04s 0/0/0 (IPv6)
                           36    0
Without the post-import option, the session is torn down as soon as the number of received routes (12) exceeds the configured prefix limit of 10.
Conclusion
The BGP prefix limit per address family feature allows ISPs to protect their network from misbehaving or misconfigured peers, and can also be used to enforce the terms of a service contract.