Forwarding between cMAG-c and MAG-u
The forwarding of control plane messages is in-band and sent using an IBCP tunnel.
IBCP
In-band control plane (IBCP) packets are sent by a residential gateway over the data path to the MAG-u, but must be handled by the cMAG-c. Examples include DHCP, DHCPv6, and ICMPv6 RS.
IBCP packets for fixed access sessions arrive before any session state is created. The MAG-u sends the initial control plane packets over GTP-U to the cMAG-c.
The following figure shows the control plane communication for fixed access.
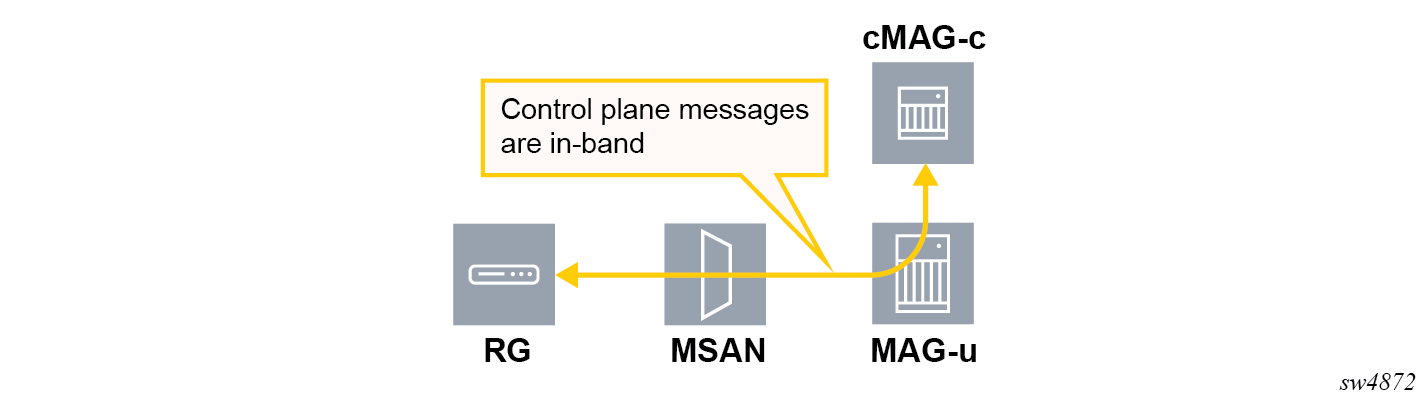
The cMAG-c installs basic PDRs for the per Layer 2 access ID IBCP session using PFCP. The MAG-u uses the SDF filters and Ethernet packet filters in the PDR to filter out control plane traffic packets; for example, to only allow PPPoE or DHCP packets. The FAR that is linked to the PDR defines the GTP-U encapsulation between the MAG-u and the cMAG-c.
Immediately after the PFCP association is created, the cMAG-c learns all Layer 2 access IDs configured on the MAG-u. Layer 2 access ID are learned via PFCP Node Report signaling; see Initial PFCP association and session setup for more information. The cMAG-c subsequently installs one GTP-U tunnel per Layer 2 access ID, using a dedicated PFCP session for unknown in-band control plane packets. That tunnel is called the per Layer 2 access ID IBCP tunnel. The Layer 2 access ID is a generalized representation of any L2 access technology such as a physical port, pseudowire port, or LAG.
Similarly, for cases where network-facing control plane traffic is required (for example, L2TP signaling for LAC/LNS), the cMAG-c learns all network instances configured on the MAG-u, and subsequently installs one GTP-U tunnel per network instance using a dedicated PFCP session for control plane packets. That tunnel is called the per network instance IBCP tunnel. A network instance is a generalized representation of a routed network, for example a plain router or IP VRF.
After the cMAG-c handles the initial control plane messages, it instructs the MAG-u to forward any subsequent control plane packets over a per-session GTP-U tunnel. The per-session GTP-U tunnel is signaled as part of the regular PFCP session for that connection.
See GTP-U encapsulation and decapsulation for more information.
GTP-U encapsulation and decapsulation
The MAG-u encapsulates a received control plane packet from the access side in a GTP-U tunnel, using the TEIDs as signaled during the PFCP session setup procedure. The MAG-u passes the received Ethernet frame as payload in the GTP-U tunnel, unmodified (that is, including the VLAN tags).
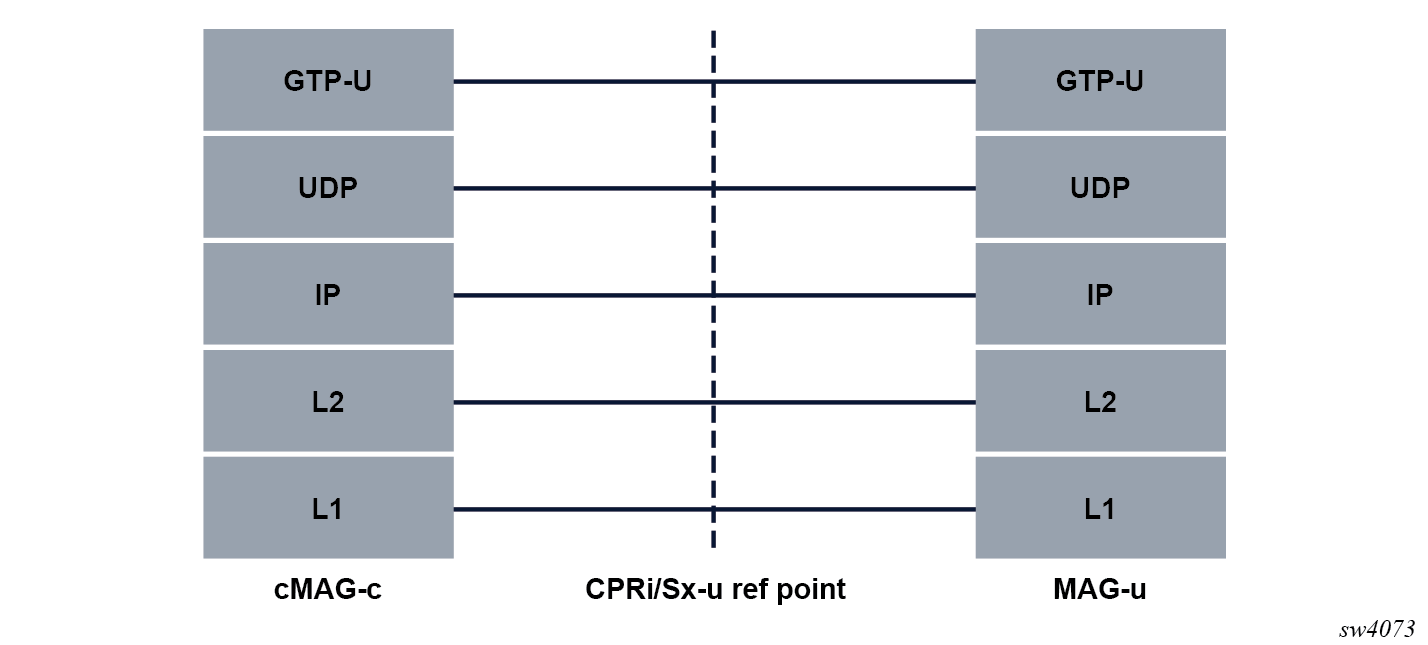
The following figure shows the protocol stack for IBCP over the CPRi interface.
- Layer 2 access ID
The cMAG-creceives IBCP packets over the Layer 2 access ID, which identifies, for example, the physical port, LAG, or pseudowire port. This uses the Logical Port type (Metadata Class 0x0200, Type 0x00) as defined in BBF TR459.
- Local MAC address 2
This is the local MAC address on the MAG-u, belonging to the Layer 2 access ID. This uses the MAC type (Metadata Class 0x0200, Type 0x01) as defined in BBF TR459.
- Network instance
This is the network instance over which the IBCP packet is received. This only applies to per-network-instance IBCP tunnels. This uses the Network Instance type (Metadata Class 0x0200, Type 0x02) as defined in BBF TR459.
- PFCP node ID
This is the PFCP node ID that identifies the MAG-u node. This uses the Ingress Network Node ID (Metadata Class 0x0000, type 0x06) as defined in RFC 9263. The MAG-u includes the PFCP node ID in this field, using the exact same contents as the PFCP Node ID IE as defined in 3GPP TS29.244, including the node ID type octet.
The cMAG-c sets up a PFCP session using the logical port in the PDR/FAR, and uses the MAC address as the source MAC when sending control plane messages. Control plane packets matching these dedicated sessions do not use NSH.
See BBF TR-459 for a description of the NSH header and metadata fields.
GTP-U runs over UDP, using port 2152, and is defined in 3GPP TS 29.281. GTP-U is extended to allow transport of Ethernet packets. This is not explicitly added in the GTP-U encoding, instead the content type is defined at tunnel setup in PFCP.
The following table describes the format of the basic GTP-U header for IBCP packets on the CPRi interface between the MAG-u and the cMAG-c.
| Bits | ||||||||
|---|---|---|---|---|---|---|---|---|
| Octets | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 |
| 1 | Version=1 | PT=0 | 0 | E | S=0 | PN=0 | ||
| 2 | Message Type = 255 | |||||||
| 3 | Message Length (1st Octet) | |||||||
| 4 | Message Length (2nd Octet) | |||||||
| 5 to 8 | TEID | |||||||
| 9 | Next Extension Header Type 1 | |||||||
- PT indicates the protocol type. The protocol type is 0 for IBCP messages on the CPRi interface.
- E indicates the presence of a meaningful value in the Next Extension Header field. When it is set to 0, the Next Extension Header field either is not present or, if present, is not interpreted. When it is set to 1, the Next Extension Header field is present, and is interpreted.
- S indicates whether the SEID field is present. IBCP messages on the CPRi interface do not contain a session ID.
- PN indicates the presence of a meaningful value in the N-PDU Number field. PN is 0 for IBCP packets on the CPRi interface. The N-PDU number is not used.
- Message Type indicates the type of the message and determines the content of the message beyond the header.
- Message Length is the total length of the packet.
- TEID is signaled during PFCP session establishment for the IBCP packets.
- Next Extension Header Type is only evaluated when E is set to 1. It defines the type of the extension header that follows this field in the GTP PDU.