Shared EG between services
To share a single EG between multiple services, ensure the following rules are not violated:
The following figure shows an example of two encrypted services using the same tunnel and EG.
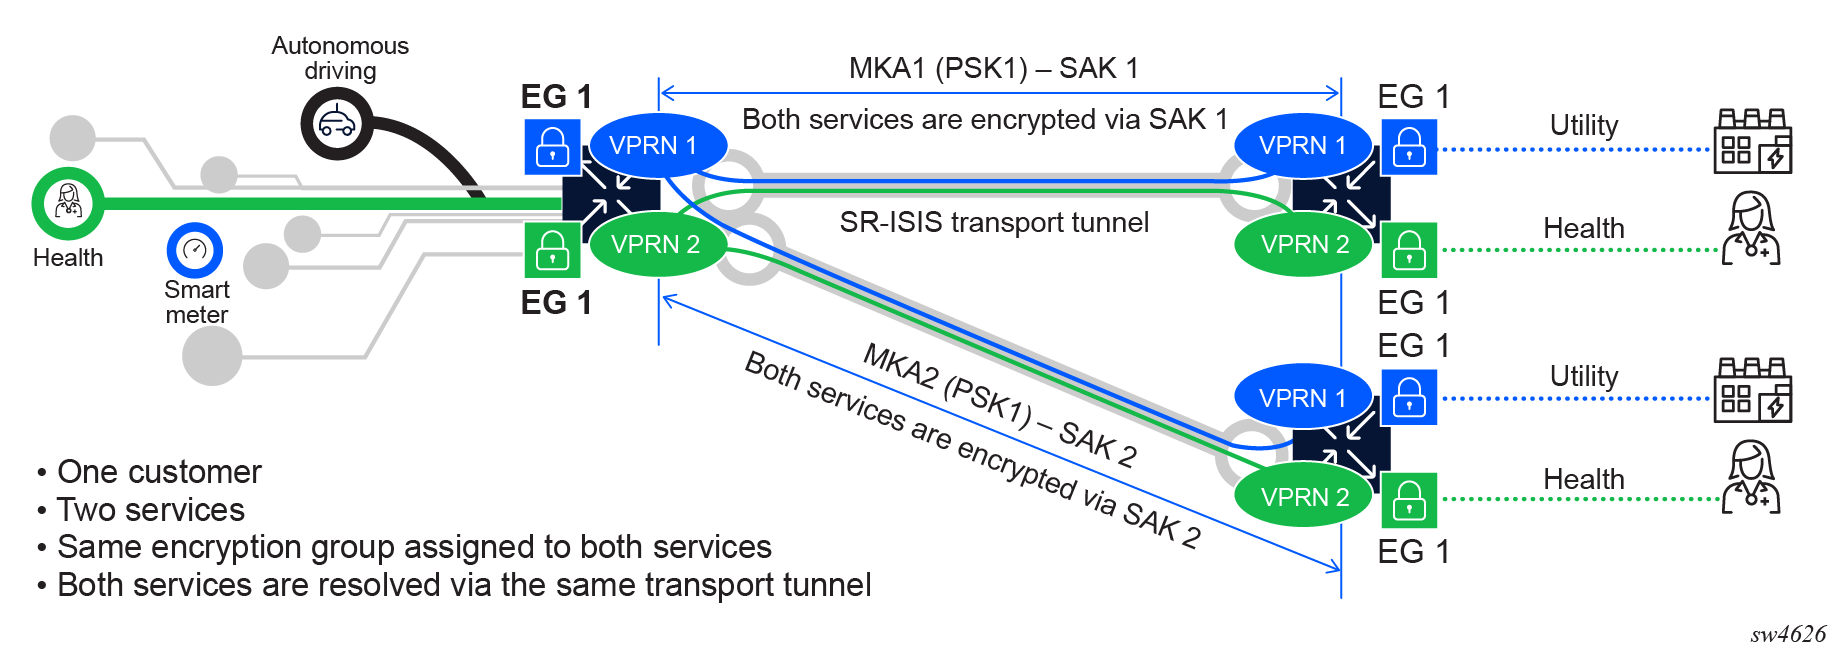
When the EG is shared between multiple services, only a single MKA session is established between the peers. Both services use that MKA session with its PSK to secure the SAK. The MKA session distributes the SAK between the peers, and both services are encrypted with the same SAK.