Unique EG between services
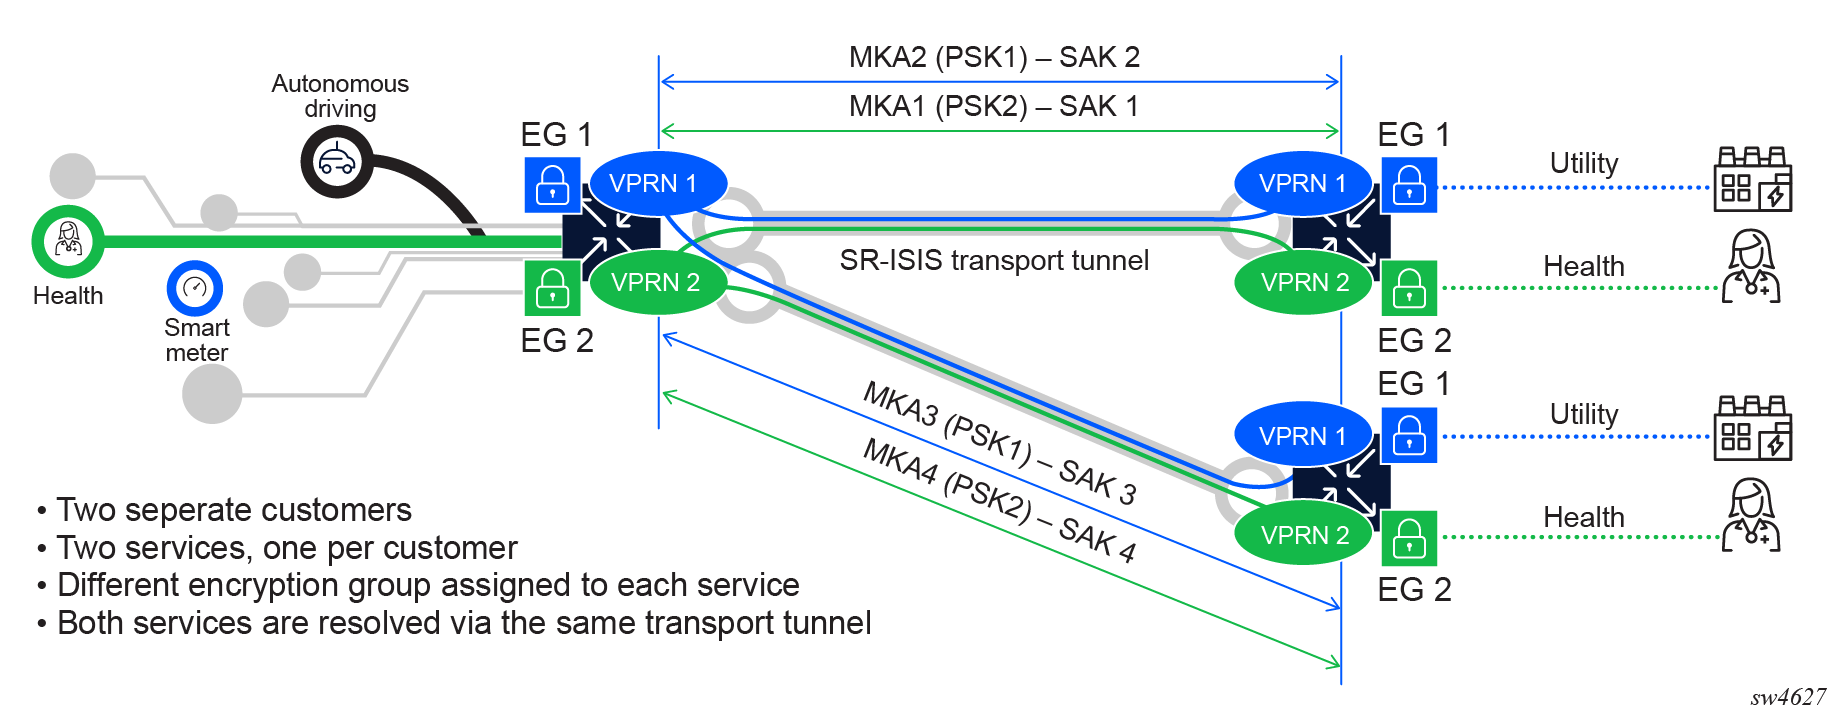
In cases where each service belongs to a unique customer, and each customer has its own security and key management requirements, it is possible to assign an EG per service. Each EG creates a dedicated MKA session with its own PSK securing its unique SAK.
The following figure shows an example of two encrypted services using the same tunnel but different EGs.