
Segment Routing with IS-IS Control Plane
This chapter provides information about Segment Routing (SR) with Intermediate System to Intermediate System (IS-IS) control plane.
Topics in this chapter include:
Applicability
This configuration in this chapter corresponds to SRL Release 26.7.1.
Overview
Segment Routing (SR) is a technology for IP/Multi-Protocol Label Switching (MPLS) networks that enables source routing. With source routing, operators can specify a forwarding path, from ingress to egress, that is independent of the shortest path determined by the Interior Gateway Protocol (IGP).
The main benefit of SR compared to other source routing protocols is that, from a control plane perspective, no signaling protocol is required. SR provides a path or tunnel, encoded as a sequential list of sub-paths or segments that are advertised within the SR domain, using extensions to well-known link state routing protocols, such as Intermediate System to Intermediate System (IS-IS) or Open Shortest Path First (OSPF).
Implementation
An SR tunnel can contain a single segment that represents the destination node, or it can contain a list of segments that the tunnel must traverse. The tunnel can be established over an IPv4/IPv6 MPLS or IPv6 data plane, encoded as a stack of MPLS labels or as a number of IPv6 addresses contained in an IPv6 extension header.
Network elements are modeled as segments. For each segment, the IGP advertises an identifier referred to as a segment ID (SID).
The two segment types are:
-
Prefix segment — A prefix segment is the Equal Cost Multi-Path ECMP-aware shortest path IGP route to a related prefix. A typical example of a prefix segment is a node segment. Prefix SIDs are globally unique and allocated from a Segment Routing Global Block (SRGB), typically multi-hop. The IGP signals the prefix SIDs. Within the SRL implementation, a node segment is either the system address or another interface address of type loopback in the Global Routing Table (GRT). IS-IS advertises node SIDs using a prefix SID sub-TLV (Type Length Value).
-
Adjacency segment — An adjacency segment represents a link between two routers. Adjacency SIDs are locally unique and allocated from a Segment Routing Local Block (SRLB), so that other routers in the SR domain can use the same label space. The IGP signals the adjacency SIDs. The SRL implementation allocates (dynamically or statically by configuration) adjacency SIDs and advertises them when the SR context within the IGP instance is enabled. IS-IS advertises adjacency SIDs in an adjacency SID sub-TLV.
To make prefix SIDs globally unique within the SR domain, an indexing mechanism is required, because production networks consist of multiple vendors and multiple products. As a result, it is often difficult to agree on a common SRGB for the prefix SIDs.
All routers within the SR domain are expected to configure and advertise the same prefix SID range for an IGP instance. The label value used by each router to represent a prefix can be local to that router by the use of an offset label, referred to as a start label: Local label (for a prefix) = (local) start label + {prefix SID index}
Within the SRL implementation, prefix Loop-Free Alternate (LFA) is supported for SR to improve the Fast Reroute (FRR) coverage. Remote LFA (RLFA) and topology independent LFA (TI-LFA) are also supported. With RLFA, SR shortest path tunnels are used as a virtual LFA or repair tunnel toward a PQ node. TI-LFA is beyond the scope of this chapter.
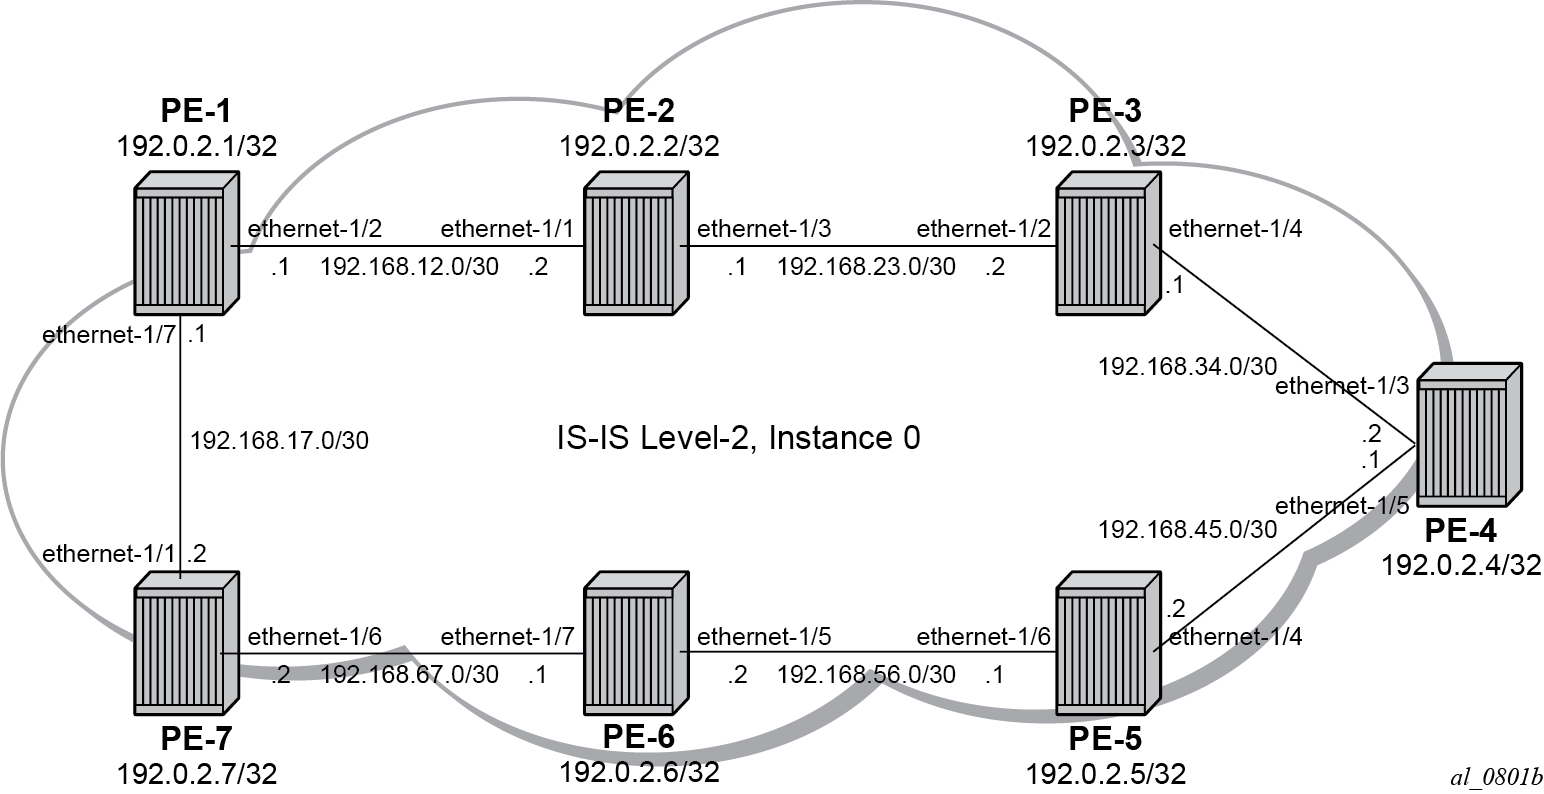
The following example uses IS-IS as an IGP protocol, with an MPLS data plane and a network instance enabled using LFA and RLFA. Example topology shows the example topology with seven PEs.
Configuration
Initial configuration
Configure the interface and the system sub interface IP addresses according to Example topology.
Select IS-IS level 2 as the IGP to distribute routing information between all PEs. All IS-IS interfaces are of type point-to-point to avoid running the Designated Router/Backup Designated Router (DR/BDR) election process.
SR configuration
Define MPLS label ranges for node and adjacency SIDs
Before enabling SR, define a static SRGB. This SRGB is required on each individual router in the SR domain and is used to allocate the prefix SIDs from.
An SRGB is not instantiated by default. For simplicity, configure the same SRGB in this example for all SR domain routers. Within the command, a start value and an end value define the size of the SRGB. The following command configures an SRGB of 1000 MPLS labels, from label 10000 to label 10999. Repeat this for all other nodes. The allocated MPLS labels are only for the prefix SIDs.
# on all PEs:
enter candidate
    system {
        mpls {
            label-ranges {
                static static-nsid {    # SRGB (global block for node SIDs)
                    start-label 10000
                    end-label 10999
Define a dedicated SRLB. This SRLB is required on each individual router in the SR domain and is used to allocate the adjacency SIDs from.
An SRLB is not instantiated by default. When configured by the operator, it is taken from the system dynamic label range (for dynamically allocated adjacency SIDs) or from the system static label range (for statically allocated adjacency SIDs). For simplicity, the same dynamic SRLB is used in this example for all SR domain routers. Within the command, a start value and an end value define the size of the SRLB. The adjacency SIDs, which are only locally unique, are taken from the SRLB.
The following command configures an SRLB of 1000 MPLS labels for dynamically allocated adjacency SIDs, from label 30000 to label 30999:
# on all PEs:
enter candidate
    system {
        mpls {
            label-ranges {
                dynamic dynamic-asid {    # SRLB (local block for adjacency SIDs)
                    start-label 30000
                    end-label 30999
The following command configures an SRLB of 1000 MPLS labels for statically allocated adjacency SIDs, from label 20000 to label 20999:
# on all PEs:
enter candidate
    system {
        mpls {
            label-ranges {
                static static-asid {    # SRLB (local block for adjacency SIDs)
                    shared false    # not shared among protocols
                    start-label 20000
                    end-label 20999
Assign the label range for node SIDs
Assign the MPLS label range for the SRGB (static-nsid) to the SR MPLS global block on the default network instance, as follows:
# on all PEs:
enter candidate
    network-instance default {
        segment-routing {
            mpls {
                global-block {
                    label-range static-nsid    # for node-SID for all protocols
Enable SR
Enable the SR context within the IS-IS instance, as follows:
# on all PEs:
enter candidate
    network-instance default {
        protocols {
            isis {
                instance 0 {
                    segment-routing {
                        mpls { }
Assign the label range for adjacency SIDs
Assign the MPLS label range for the SRLB for dynamically allocated adjacency SIDs to the dynamic label block in the isis context.
# on all PEs:
enter candidate
    network-instance default {
        protocols {
            isis {
                dynamic-label-block dynamic-asid
As an example, on PE-7 only, adjacency SIDs are allocated statically. Assign the MPLS label range for the SRLB for statically allocated adjacency SIDs to the static label block in the isis instance 0 segment-routing mpls context.
# on PE-7:
enter candidate
    network-instance default {
        protocols {
            isis {
                instance 0 {
                    segment-routing {
                        mpls {
                            static-label-block static-asid
Allocate node SIDs
Allocate a prefix SID to the prefix representing a node.
To be able to set up SR shortest path tunnels to all routers of the SR domain, each router needs to be uniquely defined within the SR domain. Therefore, allocate a node SID that is unique within the SR domain to the system address or other loopback interface in the GRT. Both an IPv4 and an IPv6 node SID can be configured, using an index. An IPv4 node SID has a label that is equal to the sum of the start label (10000), which is the first label of the SRGB on all nodes, and the index on the node.
It is possible to configure node SIDs that are protocol independent, or node SIDs that are specific for an IS-IS instance, or both. Protocol independent node SIDs can be used across multiple IGP instances. When both a protocol independent node SID and an IS-IS instance specific node SID are configured on the same node, the IS-IS instance specific node SID takes precedence and IS-IS advertises only the IS-IS instance specific node SID, not the protocol independent node SID.
Allocate a protocol independent node SID to the system address as follows:
# on all PEs:
enter candidate
    network-instance default {
        segment-routing {
            mpls {
                local-prefix-sid 1 {
                    interface system0.0
                    ipv4-label-index x    # index x for PE-x
                    node-sid true
As an example, on PE-7 only, allocate an IS-IS instance specific node SID to the system address as follows:
# on PE-7:
enter candidate
    network-instance default {
        protocols {
            isis {
                instance 0 {
                    interface system0.0 {
                        segment-routing {
                            mpls {
                                ipv4-node-sid {
                                    index 77
Allocate adjacency SIDs
# on all PEs:
enter candidate
    network-instance default {
        protocols {
            isis {
                instance 0 {
                    segment-routing {
                        mpls {
                            dynamic-adjacency-sids {
                                all-interfaces true
As an example, only on PE-7, manually allocate static adjacency SIDs for all interfaces (labels from static-asid) as follows:
# on PE-7:
enter candidate
    network-instance default {
        protocols {
            isis {
                instance 0 {
                    interface ethernet-1/1.1 {
                        segment-routing {
                            mpls {
                                ipv4-adjacency-sid {
                                    assignment static
                                    static 20071    # on PE-7 to PE-1
                                }
                            }
                        }
                    }
                    interface ethernet-1/6.1 {
                        segment-routing {
                            mpls {
                                ipv4-adjacency-sid {
                                    assignment static
                                    static 20076    # on PE-7 to PE-6
                                }
                            }
                        }
                    }
Outcome
--{ running }--[  ]--
A:admin@PE-1# info from state / system mpls label-ranges static * | as table | filter fields *
+------------------------------------------------------------------+--------+-------------+-----------+------------------+-------------+----------------+
|                               Name                               | Shared | Start-label | End-label | Allocated-labels | Free-labels |     Status     |
+==================================================================+========+=============+===========+==================+=============+================+
| static-asid                                                      | false  |       20000 |     20999 |                0 |        1000 | ready          |
| static-nsid                                                      | true   |       10000 |     10999 |                7 |         993 | ready          |
+------------------------------------------------------------------+--------+-------------+-----------+------------------+-------------+----------------+

--{ running }--[  ]--
A:admin@PE-1# info from state / system mpls label-ranges dynamic * | as table | filter fields *
+---------------------------------------------------------------------------+-------------+-----------+------------------+-------------+----------------+
|                                   Name                                    | Start-label | End-label | Allocated-labels | Free-labels |     Status     |
+===========================================================================+=============+===========+==================+=============+================+
| dynamic-asid                                                              |       30000 |     30999 |                2 |         998 | ready          |
+---------------------------------------------------------------------------+-------------+-----------+------------------+-------------+----------------+
--{ running }--[ ]--
A:admin@PE-7# info from state / system mpls label-ranges static * | as table | filter fields *
+------------------------------------------------------------------+--------+-------------+-----------+------------------+-------------+----------------+
| Name | Shared | Start-label | End-label | Allocated-labels | Free-labels | Status |
+==================================================================+========+=============+===========+==================+=============+================+
| static-asid | false | 20000 | 20999 | 2 | 998 | ready |
| static-nsid | true | 10000 | 10999 | 8 | 992 | ready |
+------------------------------------------------------------------+--------+-------------+-----------+------------------+-------------+----------------+
--{ running }--[ ]--
A:admin@PE-7# info from state / system mpls label-ranges dynamic * | as table | filter fields *
+---------------------------------------------------------------------------+-------------+-----------+------------------+-------------+----------------+
| Name | Start-label | End-label | Allocated-labels | Free-labels | Status |
+===========================================================================+=============+===========+==================+=============+================+
| dynamic-asid | 30000 | 30999 | 0 | 1000 | ready |
+---------------------------------------------------------------------------+-------------+-----------+------------------+-------------+----------------+On SR enabled PEs, the SR module resolves received prefixes with prefix SID sub TLVs present. As a result, MPLS data plane resources are consumed. The ILM is programmed with a swap operation and the label-to-next-hop-label-forwarding-entry (LTN) with a push operation, both pointing to the primary and/or LFA next-hop label forwarding entry (NHLFE). Also, an SR tunnel is added in the Tunnel Table Manager (TTM). As a result, an SR shortest path tunnel is set up to each other router that is part of the SR domain. Now, SR shortest path tunnels can be used for all users of TTM.
Each SR enabled PE advertises the locally allocated prefix SID. After the advertisement of prefix SIDs, the PE's MPLS data plane Ingress Label Mapping (ILM) is programmed with a pop operation.
Each SR enabled PE also advertises, for each formed adjacency over an IP interface, the locally allocated adjacency SID. From a data plane perspective, one local adjacency SID consumes one ILM entry, programming a pop operation (swap to IMPLICIT_NULL).
Because, in the chosen configuration, the SRGB is the same on all nodes, each node in the network can be reached using the same MPLS label. For example, the node SID for PE-5 has label 10005 on all nodes: a start label (first label of the SRGB (= 10000) + ipv4-node-sid index value on node PE-5 (= 5)). The node SID for PE-7 has label 10077 on all nodes: a start label (first label of the SRGB (= 10000) + ipv4-node-sid index value on node PE-7 (= 77). The statically allocated adjacency SIDs (label range starting with 20000) are used on PE-7, while the dynamically allocated adjacency SIDs (label range starting with 30000) are used on all other PEs.
--{ running }--[  ]--
A:admin@PE-1# show / network-instance default route-table mpls
+---------+-----------+-------------+-----------------+------------------------+----------------------+------------------+
| Label   | Operation | Type        | Next Net-Inst   | Next-hop IP (Type)     | Next-hop             | Next-hop MPLS    |
|         |           |             |                 |                        | Subinterface         | labels           |
+=========+===========+=============+=================+========================+======================+==================+
| 10001   | POP       | sr-mpls     | default         |                        |                      |                  |
| 10002   | SWAP      | sr-mpls     | N/A             | 192.168.12.2 (mpls)    | ethernet-1/2.1       | 10002            |
| 10003   | SWAP      | sr-mpls     | N/A             | 192.168.12.2 (mpls)    | ethernet-1/2.1       | 10003            |
| 10004   | SWAP      | sr-mpls     | N/A             | 192.168.12.2 (mpls)    | ethernet-1/2.1       | 10004            |
| 10005   | SWAP      | sr-mpls     | N/A             | 192.168.17.2 (mpls)    | ethernet-1/7.1       | 10005            |
| 10006   | SWAP      | sr-mpls     | N/A             | 192.168.17.2 (mpls)    | ethernet-1/7.1       | 10006            |
| 10077   | SWAP      | sr-mpls     | N/A             | 192.168.17.2 (mpls)    | ethernet-1/7.1       | 10077            |
| 30000   | SWAP      | sr-mpls     | N/A             | 192.168.12.2 (mpls)    | ethernet-1/2.1       | IMPLICIT_NULL    |
| 30001   | SWAP      | sr-mpls     | N/A             | 192.168.17.2 (mpls)    | ethernet-1/7.1       | IMPLICIT_NULL    |
+---------+-----------+-------------+-----------------+------------------------+----------------------+------------------+
--{ running }--[ ]--
A:admin@PE-1# info from state / network-instance default route-table next-hop * | as table | filter fields type ip-address subinterface mpls-encapsulation/pushed-mpls-label-stack
+--------------------------+----------------------+--------------------+--------------------------+--------------------------+--------------------------+
| Network-instance | Index | Type | Ip-address | Subinterface | Mpls-encapsulation |
| | | | | | pushed-mpls-label-stack |
+==========================+======================+====================+==========================+==========================+==========================+
| ---snip--- |
| default | 31794716 | mpls | 192.168.12.2 | ethernet-1/2.1 | IMPLICIT_NULL |
| default | 31794717 | mpls | 192.168.17.2 | ethernet-1/7.1 | IMPLICIT_NULL |
| default | 31794718 | mpls | 192.168.12.2 | ethernet-1/2.1 | 10002 |
| default | 31794719 | mpls | 192.168.12.2 | ethernet-1/2.1 | 10003 |
| default | 31794720 | mpls | 192.168.12.2 | ethernet-1/2.1 | 10004 |
| default | 31794721 | mpls | 192.168.17.2 | ethernet-1/7.1 | 10077 |
| default | 31794722 | mpls | 192.168.17.2 | ethernet-1/7.1 | 10005 |
| default | 31794723 | mpls | 192.168.17.2 | ethernet-1/7.1 | 10006 |
+--------------------------+----------------------+--------------------+--------------------------+--------------------------+--------------------------+--{ running }--[ ]--
A:admin@PE-7# show / network-instance default route-table mpls
+---------+-----------+-------------+-----------------+------------------------+----------------------+------------------+
| Label | Operation | Type | Next Net-Inst | Next-hop IP (Type) | Next-hop | Next-hop MPLS |
| | | | | | Subinterface | labels |
+=========+===========+=============+=================+========================+======================+==================+
| 10001 | SWAP | sr-mpls | N/A | 192.168.17.1 (mpls) | ethernet-1/1.1 | 10001 |
| 10002 | SWAP | sr-mpls | N/A | 192.168.17.1 (mpls) | ethernet-1/1.1 | 10002 |
| 10003 | SWAP | sr-mpls | N/A | 192.168.17.1 (mpls) | ethernet-1/1.1 | 10003 |
| 10004 | SWAP | sr-mpls | N/A | 192.168.67.1 (mpls) | ethernet-1/6.1 | 10004 |
| 10005 | SWAP | sr-mpls | N/A | 192.168.67.1 (mpls) | ethernet-1/6.1 | 10005 |
| 10006 | SWAP | sr-mpls | N/A | 192.168.67.1 (mpls) | ethernet-1/6.1 | 10006 |
| 10007 | POP | sr-mpls | default | | | |
| 10077 | POP | sr-mpls | default | | | |
| 20071 | SWAP | sr-mpls | N/A | 192.168.17.1 (mpls) | ethernet-1/1.1 | IMPLICIT_NULL |
| 20076 | SWAP | sr-mpls | N/A | 192.168.67.1 (mpls) | ethernet-1/6.1 | IMPLICIT_NULL |
+---------+-----------+-------------+-----------------+------------------------+----------------------+------------------+The tunnel table displays the prefix SIDs and adjacency SIDs, in order, within the SR domain. A tunnel with a label from static-nsid is used on each PE, to reach remote nodes. A tunnel with a label from dynamic-asid is used on each PE, except PE-7, to reach remote interfaces on the local network, while a tunnel with a label from static-asid is used on PE-7 to reach remote interfaces on the local network.
--{ running }--[  ]--
A:admin@PE-1# show / network-instance default tunnel-table ipv4
---------------------------------------------------------------------------------------------------------------------------------------------------------
IPv4 tunnel table of network-instance "default"
---------------------------------------------------------------------------------------------------------------------------------------------------------
+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+
| IPv4 Prefix  | Tunnel Type  |  Tunnel ID   |     FIB      |    Metric    |  Preference  | Last Update  |    Backup    |   Next-hop   |   Next-hop   |
|              |              |              |              |              |              |              |   Nexthops   |    (Type)    |              |
+==============+==============+==============+==============+==============+==============+==============+==============+==============+==============+
| 192.0.2.2/32 | sr-isis      | 10002        | Y            | 10           | 11           | 2026-08-     |              | 192.168.12.2 | ethernet-    |
|              |              |              |              |              |              | 21T09:50:09. |              | (mpls)       | 1/2.1        |
|              |              |              |              |              |              | 254Z         |              |              |              |
| 192.0.2.3/32 | sr-isis      | 10003        | Y            | 20           | 11           | 2026-08-     |              | 192.168.12.2 | ethernet-    |
|              |              |              |              |              |              | 21T09:50:19. |              | (mpls)       | 1/2.1        |
|              |              |              |              |              |              | 094Z         |              |              |              |
| 192.0.2.4/32 | sr-isis      | 10004        | Y            | 30           | 11           | 2026-08-     |              | 192.168.12.2 | ethernet-    |
|              |              |              |              |              |              | 21T09:50:29. |              | (mpls)       | 1/2.1        |
|              |              |              |              |              |              | 985Z         |              |              |              |
| 192.0.2.5/32 | sr-isis      | 10005        | Y            | 30           | 11           | 2026-08-     |              | 192.168.17.2 | ethernet-    |
|              |              |              |              |              |              | 21T09:51:05. |              | (mpls)       | 1/7.1        |
|              |              |              |              |              |              | 300Z         |              |              |              |
| 192.0.2.6/32 | sr-isis      | 10006        | Y            | 20           | 11           | 2026-08-     |              | 192.168.17.2 | ethernet-    |
|              |              |              |              |              |              | 21T09:51:05. |              | (mpls)       | 1/7.1        |
|              |              |              |              |              |              | 300Z         |              |              |              |
| 192.0.2.7/32 | sr-isis      | 10077        | Y            | 10           | 11           | 2026-08-     |              | 192.168.17.2 | ethernet-    |
|              |              |              |              |              |              | 21T09:51:05. |              | (mpls)       | 1/7.1        |
|              |              |              |              |              |              | 300Z         |              |              |              |
| 192.168.12.2 | sr-isis      | 30000        | Y            | 0            | 11           | 2026-08-     |              | 192.168.12.2 | ethernet-    |
| /32          |              |              |              |              |              | 21T09:49:57. |              | (mpls)       | 1/2.1        |
|              |              |              |              |              |              | 889Z         |              |              |              |
| 192.168.17.2 | sr-isis      | 30001        | Y            | 0            | 11           | 2026-08-     |              | 192.168.17.2 | ethernet-    |
| /32          |              |              |              |              |              | 21T09:49:57. |              | (mpls)       | 1/7.1        |
|              |              |              |              |              |              | 889Z         |              |              |              |
+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+
---------------------------------------------------------------------------------------------------------------------------------------------------------
8 SR-ISIS tunnels, 8 active, 0 inactive
---------------------------------------------------------------------------------------------------------------------------------------------------------
The tunnel table on PE-1 also indicates that when traffic destined for PE-7 arrives on PE-1, PE-1 pushes the MPLS label 10077 to reach destination PE-7, via the SR IS-IS tunnel with tunnel ID 10077.
PE-1 can reach destination PE-7 (with node SID 10077) via only one SR path: via PE-7.
--{ running }--[  ]--
A:admin@PE-1# show / network-instance default tunnel-table ipv4 detail
---------------------------------------------------------------------------------------------------------------------------------------------------------
Show report for network instance "default" tunnel table
---------------------------------------------------------------------------------------------------------------------------------------------------------
=========================================================================================================================================================
---snip---
Destination        : 192.0.2.7/32
Tunnel Type        : sr-isis
Tunnel ID          : 10077
Metric             : 10
Preference         : 11
Last Update        : 2026-08-21T09:51:05.300Z
FIB Status         : active
Next-hops
  192.168.17.2 (mpls) via [ethernet-1/7.1]
      pushed MPLS labels : [10077]
=========================================================================================================================================================
--{ running }--[ ]--
A:admin@PE-7# show / network-instance default tunnel-table ipv4
---------------------------------------------------------------------------------------------------------------------------------------------------------
IPv4 tunnel table of network-instance "default"
---------------------------------------------------------------------------------------------------------------------------------------------------------
+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+
| IPv4 Prefix | Tunnel Type | Tunnel ID | FIB | Metric | Preference | Last Update | Backup | Next-hop | Next-hop |
| | | | | | | | Nexthops | (Type) | |
+==============+==============+==============+==============+==============+==============+==============+==============+==============+==============+
| 192.0.2.1/32 | sr-isis | 10001 | Y | 10 | 11 | 2026-08- | | 192.168.17.1 | ethernet- |
| | | | | | | 21T09:51:05. | | (mpls) | 1/1.1 |
| | | | | | | 297Z | | | |
| 192.0.2.2/32 | sr-isis | 10002 | Y | 20 | 11 | 2026-08- | | 192.168.17.1 | ethernet- |
| | | | | | | 21T09:51:05. | | (mpls) | 1/1.1 |
| | | | | | | 297Z | | | |
| 192.0.2.3/32 | sr-isis | 10003 | Y | 30 | 11 | 2026-08- | | 192.168.17.1 | ethernet- |
| | | | | | | 21T09:51:05. | | (mpls) | 1/1.1 |
| | | | | | | 298Z | | | |
| 192.0.2.4/32 | sr-isis | 10004 | Y | 30 | 11 | 2026-08- | | 192.168.67.1 | ethernet- |
| | | | | | | 21T09:51:05. | | (mpls) | 1/6.1 |
| | | | | | | 298Z | | | |
| 192.0.2.5/32 | sr-isis | 10005 | Y | 20 | 11 | 2026-08- | | 192.168.67.1 | ethernet- |
| | | | | | | 21T09:51:05. | | (mpls) | 1/6.1 |
| | | | | | | 298Z | | | |
| 192.0.2.6/32 | sr-isis | 10006 | Y | 10 | 11 | 2026-08- | | 192.168.67.1 | ethernet- |
| | | | | | | 21T09:51:05. | | (mpls) | 1/6.1 |
| | | | | | | 298Z | | | |
| 192.168.17.1 | sr-isis | 20071 | Y | 0 | 11 | 2026-08- | | 192.168.17.1 | ethernet- |
| /32 | | | | | | 21T09:51:05. | | (mpls) | 1/1.1 |
| | | | | | | 300Z | | | |
| 192.168.67.1 | sr-isis | 20076 | Y | 0 | 11 | 2026-08- | | 192.168.67.1 | ethernet- |
| /32 | | | | | | 21T09:51:05. | | (mpls) | 1/6.1 |
| | | | | | | 300Z | | | |
+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+
---------------------------------------------------------------------------------------------------------------------------------------------------------
8 SR-ISIS tunnels, 8 active, 0 inactive
---------------------------------------------------------------------------------------------------------------------------------------------------------The tunnel table on PE-7 also indicates that when traffic destined for PE-1 arrives on PE-7, PE-7 pushes the MPLS label 10001 to reach destination PE-1, via the SR IS-IS tunnel with tunnel ID 10001.
After enabling the SR context within an IS-IS instance, the IS-IS instance advertises SR support among the IS-IS adjacencies. It propagates the router-capability-sr-capability sub TLV of the router-capability TLV, which is used to indicate the index range and the start label. It also propagates the router-capability-sr-algorithm sub TLV of the router-capability TLV, which is used to indicate the algorithm used for path calculations. Only Shortest Path First (SPF) (value 0) is defined.
Verify this as follows:
--{ running }--[  ]--
A:admin@PE-1# info from state with-context / network-instance default protocols isis instance 0 level 2
    network-instance default {
        protocols {
            isis {
                instance 0 {
                    level 2 {
                        ---snip---
                        link-state-database {
                            lsp 1920.0000.2001.00-00 {
                                ---snip---
                                tlvs {
                                    ---snip---
                                    tlv router-capability {
                                        router-capabilities {
                                            capability 0 {
                                                router-id 0.0.0.0
                                                subtlvs {
                                                    ---snip---
                                                    subtlv router-capability-sr-algorithm {
                                                        segment-routing-algorithms {
                                                            standard-algorithm [
                                                                spf
                                                            ]
                                                        }
                                                    }
                                                    subtlv router-capability-sr-capability {
                                                        segment-routing-capability {
                                                            flags [
                                                                ipv4-mpls
                                                                ipv6-mpls
                                                            ]
                                                            srgb-descriptors {
                                                                srgb-descriptor 1000 {
                                                                    label 10000
                                                                }
                                                            }
                                                        }
                                                    }
                                                }
                                            }
                                        }
                                    }
                                }
                            }
                            lsp 1920.0000.2002.00-00 {
                                ---snip---
                            }
                            lsp 1920.0000.2003.00-00 {
                                ---snip---
                            }
                            lsp 1920.0000.2004.00-00 {
                                ---snip---
                            }
                            lsp 1920.0000.2005.00-00 {
                                ---snip---
                            }
                            lsp 1920.0000.2006.00-00 {
                                ---snip---
                            }
                            lsp 1920.0000.2007.00-00 {
                                ---snip---
                            }
A similar output occurs for each router in the SR domain.
For prefix SIDs, by default, the SRL implementation sets the node flag and the no-php flag inside the ip-reachability-prefix-sid sub TLV of the extended-ipv4-reachability TLV.
--{ running }--[  ]--
A:admin@PE-1# info from state with-context / network-instance default protocols isis instance 0 level 2
    network-instance default {
        protocols {
            isis {
                instance 0 {
                    level 2 {
                        ---snip---
                        link-state-database {
                            lsp 1920.0000.2001.00-00 {
                                ---snip---
                                tlvs {
                                    ---snip---
                                    tlv extended-ipv4-reachability {
                                        extended-ipv4-reachability {
                                            prefixes {
                                                prefix 192.0.2.1/32 {
                                                    ---snip---
                                                    subtlvs {
                                                        ---snip---
                                                        subtlv ip-reachability-prefix-sid {
                                                            prefix-sids {
                                                                prefix-sid 1 {
                                                                    algorithm 0
                                                                    flags [
                                                                        node
                                                                        no-php
                                                                    ]
                                                                }
                                                            }
                                                        }
                                                    }
                                                }
                                                ---snip---
Another useful flag that can be set is the re-advertised flag. This is set when a prefix SID is propagated between levels or areas, or redistribution is in place (from another protocol).
For adjacency SIDs, by default, the SRL implementation sets the value flag in the is-reachability-adj-sid sub TLV of the extended-is-reachability TLV, meaning that the adjacency SID carries a value (as opposed to an index). Also, the local flag is set by default in the is-reachability-adj-sid sub TLV of the extended-is-reachability TLV, meaning that the adjacency SID has only local significance.
--{ running }--[  ]--
A:admin@PE-1# info from state with-context / network-instance default protocols isis instance 0 level 2
    network-instance default {
        protocols {
            isis {
                instance 0 {
                    level 2 {
                        ---snip---
                        link-state-database {
                            lsp 1920.0000.2001.00-00 {
                                ---snip---
                                tlvs {
                                    ---snip---
                                    tlv extended-is-reachability {
                                        extended-is-reachability {
                                            neighbors {
                                                neighbor 1920.0000.2002 {
                                                    instances {
                                                        instance 0 {
                                                            metric 10
                                                            subtlvs {
                                                                subtlv is-reachability-adj-sid {
                                                                    adjacency-sids {
                                                                        adjacency-sid 30000 {
                                                                            weight 0
                                                                            flags [
                                                                                value
                                                                                local
                                                                            ]
                                                                        }
                                                                    }
                                                                }
                                                                subtlv is-reachability-ipv4-interface-address {
                                                                    ipv4-interface-address {
                                                                        address [
                                                                            192.168.12.1
                                                                        ]
                                                                    }
                                                                }
                                                                subtlv is-reachability-ipv4-neighbor-address {
                                                                    ipv4-neighbor-address {
                                                                        address [
                                                                            192.168.12.2
                                                                        ]
                                                                    }
                                                                }
                                                            }
                                                        }
                                                    }
                                                }
                                                neighbor 1920.0000.2007 {
                                                    ---snip---
                                                                subtlv is-reachability-adj-sid {
                                                                    adjacency-sids {
                                                                        adjacency-sid 30001 {
                                                                            weight 0
                                                                            flags [
                                                                                value
                                                                                local
                                                                            ]
                                                                        }
                                                                    }
                                                                }
                                                                ---snip--
Configuration of an IP VRF
In the network topology of Example topology, each router of the SR domain has a full mesh of SR shortest path tunnels to the other routers.
Configuration with SR only
Configure BGP on PE-1 and PE-7:
# on PE-1 and PE-7:
enter candidate
    network-instance default {
        protocols {
            bgp {
                admin-state enable
                autonomous-system 64496
                router-id 192.0.2.1    # 192.0.2.7 on PE-7
                afi-safi l3vpn-ipv4-unicast {
                    admin-state enable
                }
                afi-safi l3vpn-ipv6-unicast {
                    admin-state enable
                }
                group IBGP {
                    admin-state enable
                    peer-as 64496
                }
                neighbor 192.0.2.7 {    # 192.0.2.1 on PE-7
                    admin-state enable
                    peer-group IBGP
                }
Configure a loopback interface on PE-1 and PE-7:
# on PE-1 and PE-7:
enter candidate
    interface lo0 {
        admin-state enable
        subinterface 0 {
            admin-state enable
            description loopback-interface-in-ip-vrf
            ipv4 {
                admin-state enable
                address 10.10.100.1/32 {    # 10.10.100.7/32 on PE-7
                    primary
                }
            }
            ipv6 {
                admin-state enable
                address 2001:db8::10:100:1/128 {    # 2001:db8::10:100:7/128 on PE-7
                }
            }
Define a dedicated dynamic MPLS label range for VRFs on all PEs that belong to ip-vrf-100 (here PE-1 and PE-7):
# on PE-1 and PE-7:
enter candidate
    system {
        mpls {
            label-ranges {
                dynamic dynamic-vrfs {
                    start-label 50000
                    end-label 50999
Assign the MPLS label range for VRFs to the network instance's dynamic label block:
# on PE-1 and PE-7:
enter candidate
    system {
        mpls {
            services {
                network-instance {
                    dynamic-label-block dynamic-vrfs
Configure network instance ip-vrf-100 on PE-1 and PE-7 that makes use of the loopback interface lo0.0 and SR IS-IS tunnels as next hop:
# on PE-1 and PE-7:
enter candidate
    network-instance ip-vrf-100 {
        type ip-vrf
        admin-state enable
            interface lo0.0 {
            interface-ref {
                interface lo0
                subinterface 0
            }
        }
        protocols {
                bgp-ipvpn {
                bgp-instance 1 {
                    admin-state enable
                    ecmp 2
                    mpls {
                        next-hop-resolution {
                            allowed-tunnel-types [
                                sr-isis
                            ]
                        }
                    }
                }
            }
            bgp-vpn {
                bgp-instance 1 {
                    route-distinguisher {
                        rd 192.0.2.1:100    # 192.0.2.7:100 on PE-7
                    }
                    route-target {
                        export-rt target:64496:100
                        import-rt target:64496:100
                    }
                }
            }
        }
Verify the IP connectivity in ip-vrf-100 as follows:
# on PE-1:
ping 10.10.100.7 network-instance ip-vrf-100 -c 3

Using network instance ip-vrf-100
PING 10.10.100.7 (10.10.100.7) 56(84) bytes of data.
64 bytes from 10.10.100.7: icmp_seq=1 ttl=64 time=5.31 ms
64 bytes from 10.10.100.7: icmp_seq=2 ttl=64 time=4.34 ms
64 bytes from 10.10.100.7: icmp_seq=3 ttl=64 time=3.95 ms

--- 10.10.100.7 ping statistics ---
3 packets transmitted, 3 received, 0% packet loss, time 2002ms
rtt min/avg/max/mdev = 3.951/4.533/5.305/0.568 ms
The route table in ip-vrf-100 on PE-1 indicates that traffic destined for 10.10.100.7/32 (connected to PE-7) runs via the SR IS-IS tunnel to PE-7.
--{ running }--[  ]--
A:admin@PE-1# show / network-instance ip-vrf-100 ipv4 route 10.10.100.7/32
=========================================================================================================================================================
IPv4-unicast route table for ip-vrf network-instance: ip-vrf-100
---------------------------------------------------------------------------------------------------------------------------------------------------------
Flags: > (best), * (unviable), ! (failed)
     : L (leaked route from another network-instance)
     : B (backup NHG active and displayed)
     : S (statistics supported)
     : D (dynamic LB), R (resilient LB)
---------------------------------------------------------------------------------------------------------------------------------------------------------
Prefix               Route Type   Metric   Pref    Flags    Next-Hop(s)
---------------------------------------------------------------------------------------------------------------------------------------------------------
10.10.100.7/32       bgp-ipvpn    10       170     >        192.0.2.7(tunnel:sr-isis, label:50000)
The detail of the route table in ip-vrf-100 on PE-1 indicates also the tunnel ID.
--{ running }--[  ]--
A:admin@PE-1# show / network-instance ip-vrf-100 ipv4 route 10.10.100.7/32 detail
=========================================================================================================================================================
Prefix: 10.10.100.7/32
---------------------------------------------------------------------------------------------------------------------------------------------------------
Active                : yes
Route Type            : bgp-ipvpn
Route Owner           : bgp_ipvpn_mgr, 2026-08-21T10:32:04.645Z (20 minutes ago)
Id                    : 0
Leakable              : no
Leaked                : no
Metric                : 10
Preference            : 170
Internal Tags         : none
Dynamic LB            : no
Resilient Hash        : no
FIB Suppressed        : no
FIB Failed            : no
Next-Hop-Group        : 31794730
  Net-Instance        : ip-vrf-100
  FIB Failed          : no
  Primary NH Count    : 1
  Backup NH Count     : 0
  Primary NH          : 31794726
    LB Weight         : 1
    Type              : indirect
    IP Address        : 192.0.2.7
    Resolved          : yes
    Resolving Tunnel  : 192.0.2.7/32(sr-isis, 10077)
    MPLS Lbl Stack    : 50000
The route in ip-vrf-100 on PE-1 indicates the network instance label.
--{ running }--[  ]--
A:admin@PE-1# show / network-instance ip-vrf-100 ipv4 route 10.10.100.7/32
=========================================================================================================================================================
IPv4-unicast route table for ip-vrf network-instance: ip-vrf-100
---------------------------------------------------------------------------------------------------------------------------------------------------------
Flags: > (best), * (unviable), ! (failed)
     : L (leaked route from another network-instance)
     : B (backup NHG active and displayed)
     : S (statistics supported)
     : D (dynamic LB), R (resilient LB)
---------------------------------------------------------------------------------------------------------------------------------------------------------
Prefix               Route Type   Metric   Pref    Flags    Next-Hop(s)
---------------------------------------------------------------------------------------------------------------------------------------------------------
10.10.100.7/32       bgp-ipvpn    10       170     >        192.0.2.7(tunnel:sr-isis, label:50000)
Configuration with SR and LFA
Enable prefix LFA within the IS-IS context to enable LFA FRR protection. Extend the remote LFA next-hop resolution path entry to RTM so that the tunnel can be used in SPF decisions.
# on all PEs:
enter candidate
    network-instance default {
        protocols {
            isis {
                instance 0 {
                    loopfree-alternate {
                        admin-state enable
                        augment-route-table true    # display backup NH
On PE-1, next-hop LFA protection is present for node PE-4, node PE-5, and the link between PE-4 and PE-5, as follows. Similar next-hop LFA protection is present on the other PEs (for other nodes or links).
--{ running }--[  ]--
A:admin@PE-1# show / network-instance default ipv4 route
=========================================================================================================================================================
IPv4-unicast route table for default network-instance
---------------------------------------------------------------------------------------------------------------------------------------------------------
Flags: > (best), * (unviable), ! (failed)
     : L (leaked route from another network-instance)
     : B (backup NHG active and displayed)
     : S (statistics supported)
     : D (dynamic LB), R (resilient LB)
---------------------------------------------------------------------------------------------------------------------------------------------------------
Prefix               Route Type   Metric   Pref    Flags    Next-Hop(s)
---------------------------------------------------------------------------------------------------------------------------------------------------------
192.0.2.2/32         isis         10       18      >        192.168.12.2(ethernet-1/2.1)
192.0.2.3/32         isis         20       18      >        192.168.12.2(ethernet-1/2.1)
192.0.2.4/32         isis         30       18      >        192.168.12.2(ethernet-1/2.1)
                                                              backup:192.168.17.2(ethernet-1/7.1)
192.0.2.5/32         isis         30       18      >        192.168.17.2(ethernet-1/7.1)
                                                              backup:192.168.12.2(ethernet-1/2.1)
192.0.2.6/32         isis         20       18      >        192.168.17.2(ethernet-1/7.1)
192.0.2.7/32         isis         10       18      >        192.168.17.2(ethernet-1/7.1)
192.168.12.0/30      local        0        0       >        192.168.12.1(ethernet-1/2.1)
192.168.17.0/30      local        0        0       >        192.168.17.1(ethernet-1/7.1)
192.168.23.0/30      isis         20       18      >        192.168.12.2(ethernet-1/2.1)
192.168.34.0/30      isis         30       18      >        192.168.12.2(ethernet-1/2.1)
192.168.45.0/30      isis         40       18      >        192.168.12.2(ethernet-1/2.1)
                                                              backup:192.168.17.2(ethernet-1/7.1)
192.168.56.0/30      isis         30       18      >        192.168.17.2(ethernet-1/7.1)
192.168.67.0/30      isis         20       18      >        192.168.17.2(ethernet-1/7.1)
PE-1 can reach destination PE-4 (with node SID 10004) via two different SR paths: one via PE-7 and one via PE-2. Similar for destination PE-5.
--{ running }--[  ]--
A:admin@PE-1# show / network-instance default tunnel-table ipv4 detail
---------------------------------------------------------------------------------------------------------------------------------------------------------
Show report for network instance "default" tunnel table
---------------------------------------------------------------------------------------------------------------------------------------------------------
=========================================================================================================================================================
---snip---
Destination        : 192.0.2.4/32
Tunnel Type        : sr-isis
Tunnel ID          : 10004
Metric             : 30
Preference         : 11
Last Update        : 2026-08-21T10:37:47.960Z
FIB Status         : active
Next-hops
  192.168.12.2 (mpls) via [ethernet-1/2.1]
      pushed MPLS labels : [10004]
Backup Next-hops
  192.168.17.2 (mpls) via [ethernet-1/7.1]
      pushed MPLS labels : [10004]
=========================================================================================================================================================
--{ running }--[ ]--
A:admin@PE-1# info from state / network-instance default route-table next-hop * | as table | filter fields type ip-address subinterface mpls-encapsulation/pushed-mpls-label-stack
+--------------------------+----------------------+--------------------+--------------------------+--------------------------+--------------------------+
| Network-instance | Index | Type | Ip-address | Subinterface | Mpls-encapsulation |
| | | | | | pushed-mpls-label-stack |
+==========================+======================+====================+==========================+==========================+==========================+
| ---snip--- |
| default | 31794716 | mpls | 192.168.12.2 | ethernet-1/2.1 | IMPLICIT_NULL |
| default | 31794717 | mpls | 192.168.17.2 | ethernet-1/7.1 | IMPLICIT_NULL |
| default | 31794718 | mpls | 192.168.12.2 | ethernet-1/2.1 | 10002 |
| default | 31794719 | mpls | 192.168.12.2 | ethernet-1/2.1 | 10003 |
| default | 31794721 | mpls | 192.168.17.2 | ethernet-1/7.1 | 10077 |
| default | 31794723 | mpls | 192.168.17.2 | ethernet-1/7.1 | 10006 |
| ---snip--- |
| default | 31794729 | mpls | 192.168.17.2 | ethernet-1/7.1 | 10004 |
| default | 31794730 | mpls | 192.168.12.2 | ethernet-1/2.1 | 10004 |
| default | 31794731 | mpls | 192.168.12.2 | ethernet-1/2.1 | 10005 |
| default | 31794732 | mpls | 192.168.17.2 | ethernet-1/7.1 | 10005 |
+--------------------------+----------------------+--------------------+--------------------------+--------------------------+--------------------------+When a failure occurs on the primary SR path (only applicable for prefix PE-4/PE-5 and the link between PE-4 and PE-5), the traffic takes the LFA backup SR path to the destination using the same MPLS label value.
Configuration with SR, LFA, and RLFA
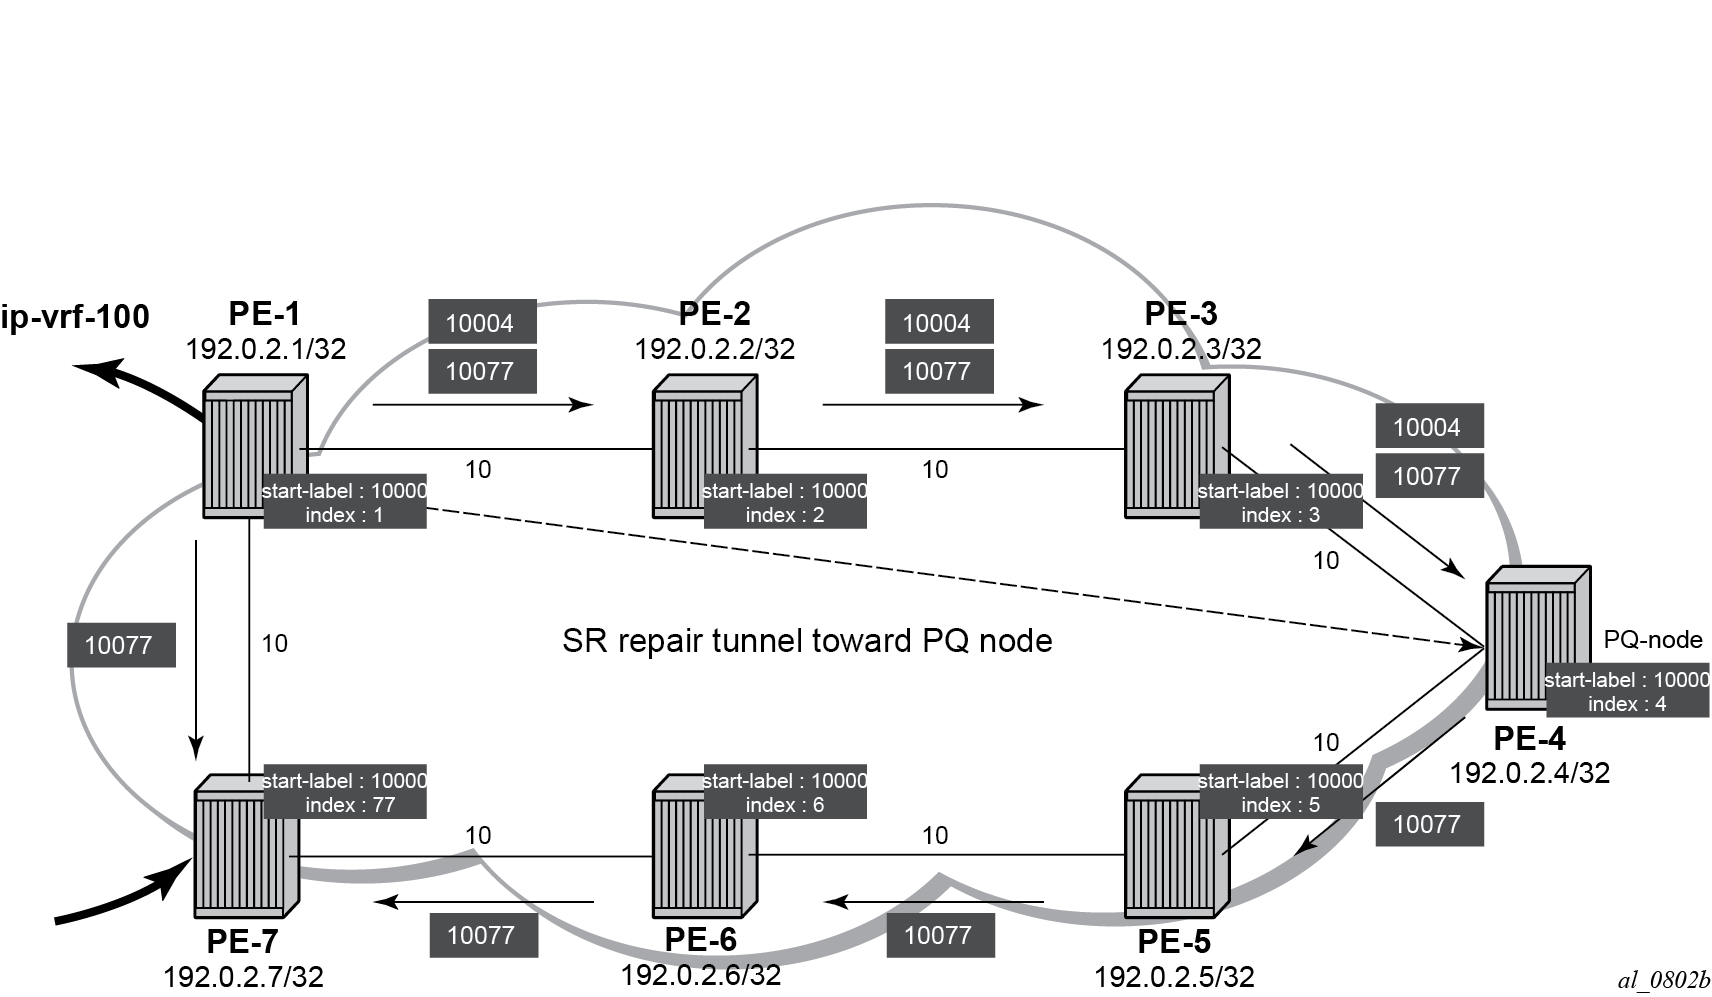
To extend the LFA FRR coverage, for example, to find an LFA protection for node PE-7, which is one of the ip-vrf-100 endpoints, RLFA can be enabled. RLFA creates a virtual LFA by using a repair tunnel to carry packets to a point in the network from where they are not looped back to the source, but forwarded (SPF-based) toward the destination prefix.
The RLFA implementation uses the PQ algorithm. The node where RLFA is configured (PE-1 in this example) computes an extended P-space and a Q-space. The intersection of both spaces contains the PQ-nodes. This PQ node is the destination node of the repair tunnel using an SR shortest path tunnel. To compute both spaces, SPF is used.
In this example, IS-IS is used as the IGP, using a default metric value of 10 for all links. With the assumption that the link between PE-1 and PE-7 is broken, the calculation of both the extended P-space and the Q-space at PE-1 is as follows:
-
extended P-space — An SPF computed from node PE-1 and rooted at PE-2. It is used to calculate the set of routers that are reachable without any path transiting the protected link between PE-1 and PE-7. The following nodes belong to the extended P-space: PE-2, PE-3, PE-4, and PE-5.
-
Q-space — A reverse SPF computed from PE-1 and rooted from PE-7 (acting as destination proxy). It is used to calculate the set of routers that can reach PE-7 without transiting the protected link between PE-1 and PE-7. The nodes PE-4, PE-5, and PE-6 belong to the Q-space.
Possible PQ-nodes are PE-4 or PE-5, because they are in the intersection of both spaces.
RLFA is configured as follows:
# on all PEs:
enter candidate
    network-instance default {
        protocols {
            isis {
                instance 0 {
                    loopfree-alternate {
                        admin-state enable
                        augment-route-table true
                        remote-lfa {
                            admin-state enable
                            node-protect {
                                admin-state enable
                            }
                        }
On PE-1, the nodes PE-2, PE-3, PE-6, and PE-7 now have RLFA protection, whereas PE-4 and PE-5 have LFA protection. Similar next-hop LFA or RLFA protection is present on the other PEs (for other nodes or links).
--{ running }--[  ]--
A:admin@PE-1# info from state / network-instance default route-table next-hop * | as table | filter fields type ip-address subinterface mpls-encapsulation/pushed-mpls-label-stack
+--------------------------+----------------------+--------------------+--------------------------+--------------------------+--------------------------+
|     Network-instance     |        Index         |        Type        |        Ip-address        |       Subinterface       |    Mpls-encapsulation    |
|                          |                      |                    |                          |                          | pushed-mpls-label-stack  |
+==========================+======================+====================+==========================+==========================+==========================+
| ---snip---                                                                                                                                            |
| default                  |             31794729 | mpls               | 192.168.17.2             | ethernet-1/7.1           | 10004                    |
| default                  |             31794730 | mpls               | 192.168.12.2             | ethernet-1/2.1           | 10004                    |
| default                  |             31794731 | mpls               | 192.168.12.2             | ethernet-1/2.1           | 10005                    |
| default                  |             31794732 | mpls               | 192.168.17.2             | ethernet-1/7.1           | 10005                    |
| default                  |             31794733 | mpls               | 192.168.17.2             | ethernet-1/7.1           | 10002 10005              |
| default                  |             31794734 | mpls               | 192.168.12.2             | ethernet-1/2.1           | 10002                    |
| default                  |             31794735 | mpls               | 192.168.17.2             | ethernet-1/7.1           | 10003 10005              |
| default                  |             31794736 | mpls               | 192.168.12.2             | ethernet-1/2.1           | 10003                    |
| default                  |             31794737 | mpls               | 192.168.12.2             | ethernet-1/2.1           | 10006 10004              |
| default                  |             31794738 | mpls               | 192.168.17.2             | ethernet-1/7.1           | 10006                    |
| default                  |             31794739 | mpls               | 192.168.12.2             | ethernet-1/2.1           | 10077 10004              |
| default                  |             31794740 | mpls               | 192.168.17.2             | ethernet-1/7.1           | 10077                    |
| default                  |             31794741 | mpls               | 192.168.12.2             | ethernet-1/2.1           | IMPLICIT_NULL            |
| default                  |             31794742 | mpls               | 192.168.17.2             | ethernet-1/7.1           | IMPLICIT_NULL            |
+--------------------------+----------------------+--------------------+--------------------------+--------------------------+--------------------------+
PE-1 can reach destination PE-7 (with node SID 10077) via two different SR paths: one via PE-7 and one via PE-2, which excludes the link between PE-1 and PE-7. Similar for destination PE-6. PE-1 can reach destination PE-2 (with node SID 10002) via two different SR paths: one via PE-2 and one via PE-7, which excludes the link between PE-1 and PE-2. Similar for destination PE-3.
--{ running }--[  ]--
A:admin@PE-1# show / network-instance default tunnel-table ipv4 detail
---------------------------------------------------------------------------------------------------------------------------------------------------------
Show report for network instance "default" tunnel table
---------------------------------------------------------------------------------------------------------------------------------------------------------
=========================================================================================================================================================
---snip---
Destination        : 192.0.2.7/32
Tunnel Type        : sr-isis
Tunnel ID          : 10077
Metric             : 10
Preference         : 11
Last Update        : 2026-08-21T10:42:46.046Z
FIB Status         : active
Next-hops
  192.168.17.2 (mpls) via [ethernet-1/7.1]
      pushed MPLS labels : [10077]
Backup Next-hops
  192.168.12.2 (mpls) via [ethernet-1/2.1]
      pushed MPLS labels : [10077, 10004]
=========================================================================================================================================================
The main difference between normal prefix LFA and RLFA is that for RLFA a two-MPLS label stack is pushed by the head-end node (PE-1). The top label is the SR-label to reach the PQ node (for example, 10004 for the PQ node PE-4) and the bottom label is the SR-label to reach the destination node (for example, 10077 for destination node PE-7). The notation inside the show command output is [ bottom-label, top-label. ].
RLFA traffic path during protection illustrates the RLFA traffic path protecting the link between PE-1 and PE-7 for traffic from PE-1 to PE-7:
Configuration with SR and LDP, without LFA and RLFA
To show the impact of protocol preference within TTM, configure LDP on PE-1 and PE-7, next to SR. This can be useful in case of migration scenarios from a non-SR environment toward a hybrid environment having LDP and SR enabled.
In the following, delete LFA (and RLFA) to simplify the scenario:
# on all PEs:
enter candidate
    network-instance default {
        protocols {
            isis {
                instance 0 {
                    delete loopfree-alternate
Define a dedicated dynamic MPLS label range for LDP on all PEs:
# on all PEs:
enter candidate
    system {
        mpls {
            label-ranges {
                dynamic dynamic-ldp {
                    start-label 60000
                    end-label 60999
Assign the MPLS label range for LDP to the LDP dynamic label block and configure LDP discovery of interfaces on all PEs.
# on all PEs:
enter candidate
    network-instance default {
        protocols {
            ldp {
                admin-state enable
                dynamic-label-block dynamic-ldp
                discovery {
                    interfaces {
                        interface ethernet-1/2.1 {    # other interface on other PEs
                            ipv4 {
                                admin-state enable
                            }
                        }
                        interface ethernet-1/7.1 {    # other interface on other PEs
                            ipv4 {
                                admin-state enable
                            }
                        }
                    }
                }
By enabling LDP, the MPLS label mapping includes entries for LDP, with labels from dynamic-ldp.
Also the TTM changes. With ip-vrf-100 between PE-1 and PE-7 as an example, only those two specific network instance endpoints are displayed.
An LDP LSP and an SR shortest path tunnel (using IS-IS) are present and active for the same destination.
--{ + running }--[  ]--
A:admin@PE-1# show / network-instance default tunnel-table ipv4 192.0.2.7/32
---------------------------------------------------------------------------------------------------------------------------------------------------------
IPv4 tunnel table of network-instance "default"
---------------------------------------------------------------------------------------------------------------------------------------------------------
+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+
| IPv4 Prefix  | Tunnel Type  |  Tunnel ID   |     FIB      |    Metric    |  Preference  | Last Update  |    Backup    |   Next-hop   |   Next-hop   |
|              |              |              |              |              |              |              |   Nexthops   |    (Type)    |              |
+==============+==============+==============+==============+==============+==============+==============+==============+==============+==============+
| 192.0.2.7/32 | ldp          | 65540        | Y            | 10           | 9            | 2026-08-     |              | 192.168.17.2 | ethernet-    |
|              |              |              |              |              |              | 21T10:56:34. |              | (mpls)       | 1/7.1        |
|              |              |              |              |              |              | 592Z         |              |              |              |
| 192.0.2.7/32 | sr-isis      | 10077        | Y            | 10           | 11           | 2026-08-     |              | 192.168.17.2 | ethernet-    |
|              |              |              |              |              |              | 21T10:54:40. |              | (mpls)       | 1/7.1        |
|              |              |              |              |              |              | 193Z         |              |              |              |
+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+
---------------------------------------------------------------------------------------------------------------------------------------------------------
1 LDP tunnels, 1 active, 0 inactive
1 SR-ISIS tunnels, 1 active, 0 inactive
---------------------------------------------------------------------------------------------------------------------------------------------------------
--{ running }--[ ]--
A:admin@PE-7# show / network-instance default tunnel-table ipv4 192.0.2.1/32
---------------------------------------------------------------------------------------------------------------------------------------------------------
IPv4 tunnel table of network-instance "default"
---------------------------------------------------------------------------------------------------------------------------------------------------------
+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+
| IPv4 Prefix | Tunnel Type | Tunnel ID | FIB | Metric | Preference | Last Update | Backup | Next-hop | Next-hop |
| | | | | | | | Nexthops | (Type) | |
+==============+==============+==============+==============+==============+==============+==============+==============+==============+==============+
| 192.0.2.1/32 | ldp | 65540 | Y | 10 | 9 | 2026-08- | | 192.168.17.1 | ethernet- |
| | | | | | | 21T10:56:34. | | (mpls) | 1/1.1 |
| | | | | | | 335Z | | | |
| 192.0.2.1/32 | sr-isis | 10001 | Y | 10 | 11 | 2026-08- | | 192.168.17.1 | ethernet- |
| | | | | | | 21T09:51:05. | | (mpls) | 1/1.1 |
| | | | | | | 297Z | | | |
+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+--------------+
---------------------------------------------------------------------------------------------------------------------------------------------------------
1 LDP tunnels, 1 active, 0 inactive
1 SR-ISIS tunnels, 1 active, 0 inactive
---------------------------------------------------------------------------------------------------------------------------------------------------------The LDP LSP is preferred by default (lower preference value), but as long as the allowed-tunnel-types does not include ldp, it is not chosen.
--{ running }--[  ]--
A:admin@PE-1# show / network-instance ip-vrf-100 ipv4 route 10.10.100.7/32 detail
=========================================================================================================================================================
Prefix: 10.10.100.7/32
---------------------------------------------------------------------------------------------------------------------------------------------------------
Active                : yes
Route Type            : bgp-ipvpn
Route Owner           : bgp_ipvpn_mgr, 2026-08-21T10:32:04.645Z (20 minutes ago)
Id                    : 0
Leakable              : no
Leaked                : no
Metric                : 10
Preference            : 170
Internal Tags         : none
Dynamic LB            : no
Resilient Hash        : no
FIB Suppressed        : no
FIB Failed            : no
Next-Hop-Group        : 31794730
  Net-Instance        : ip-vrf-100
  FIB Failed          : no
  Primary NH Count    : 1
  Backup NH Count     : 0
  Primary NH          : 31794726
    LB Weight         : 1
    Type              : indirect
    IP Address        : 192.0.2.7
    Resolved          : yes
    Resolving Tunnel  : 192.0.2.7/32(sr-isis, 10077)
    MPLS Lbl Stack    : 50000
--{ running }--[ ]--
A:admin@PE-1# show / network-instance ip-vrf-100 ipv4 route 10.10.100.7/32
=========================================================================================================================================================
IPv4-unicast route table for ip-vrf network-instance: ip-vrf-100
---------------------------------------------------------------------------------------------------------------------------------------------------------
Flags: > (best), * (unviable), ! (failed)
: L (leaked route from another network-instance)
: B (backup NHG active and displayed)
: S (statistics supported)
: D (dynamic LB), R (resilient LB)
---------------------------------------------------------------------------------------------------------------------------------------------------------
Prefix Route Type Metric Pref Flags Next-Hop(s)
---------------------------------------------------------------------------------------------------------------------------------------------------------
10.10.100.7/32 bgp-ipvpn 10 170 > 192.0.2.7(tunnel:sr-isis, label:50000)The LDP LSP is chosen, when allowed-tunnel-types also includes ldp. Because this is an IP VRF specific parameter, the operator has the choice to only configure this on one specific IP VRF endpoint. From a migration point of view, a smooth and easy SR migration is possible, not affecting any other deployed network instances on this node.
# on PE-1 and PE-7:
enter candidate
    network-instance ip-vrf-100 {
        protocols {
            bgp-ipvpn {
                bgp-instance 1 {
                    mpls {
                        next-hop-resolution {
                            allowed-tunnel-types [
                                ldp
                                sr-isis
ip-vrf-100 on node PE-1 now uses the LDP LSP to reach node PE-7.
--{ + running }--[  ]--
A:admin@PE-1# show / network-instance ip-vrf-100 ipv4 route 10.10.100.7/32 detail
=========================================================================================================================================================
Prefix: 10.10.100.7/32
---------------------------------------------------------------------------------------------------------------------------------------------------------
Active                : yes
Route Type            : bgp-ipvpn
Route Owner           : bgp_ipvpn_mgr, 2026-08-21T10:58:19.019Z (2 minutes ago)
Id                    : 0
Leakable              : no
Leaked                : no
Metric                : 10
Preference            : 170
Internal Tags         : none
Dynamic LB            : no
Resilient Hash        : no
FIB Suppressed        : no
FIB Failed            : no
Next-Hop-Group        : 31794756
  Net-Instance        : ip-vrf-100
  FIB Failed          : no
  Primary NH Count    : 1
  Backup NH Count     : 0
  Primary NH          : 31794758
    LB Weight         : 1
    Type              : indirect
    IP Address        : 192.0.2.7
    Resolved          : yes
    Resolving Tunnel  : 192.0.2.7/32(ldp, 65540)
    MPLS Lbl Stack    : 50000
--{ + running }--[ ]--
A:admin@PE-1# show / network-instance ip-vrf-100 ipv4 route 10.10.100.7/32
=========================================================================================================================================================
IPv4-unicast route table for ip-vrf network-instance: ip-vrf-100
---------------------------------------------------------------------------------------------------------------------------------------------------------
Flags: > (best), * (unviable), ! (failed)
: L (leaked route from another network-instance)
: B (backup NHG active and displayed)
: S (statistics supported)
: D (dynamic LB), R (resilient LB)
---------------------------------------------------------------------------------------------------------------------------------------------------------
Prefix Route Type Metric Pref Flags Next-Hop(s)
---------------------------------------------------------------------------------------------------------------------------------------------------------
10.10.100.7/32 bgp-ipvpn 10 170 > 192.0.2.7(tunnel:ldp, label:50000)Conclusion
SR is a technique using extensions of the existing link state protocols, and using existing MPLS or IPv6 infrastructure as the data plane. It is a source routing technique without the need to run an extra signaling protocol. SR also avoids other scaling restrictions, such as midpoint state. SR is simple to control and operate because the intelligence and state are part of the packet, not held by the network. Other benefits are that SR can be introduced in an incremental way using different migration scenarios to assure a smooth transition.